NeuralWired.com | Elite-class frontier technology intelligence for technologists, executives, founders, policy professionals, and investors shaping what comes next. This analysis is part of our ongoing AI Security coverage series.
Breaking Analysis · AI Supply Chain Security · April 4, 2026
The Mercor LiteLLM supply chain breach wasn’t a fluke it was the inevitable collision of AI infrastructure’s explosive growth and its catastrophic security debt. Here’s everything you need to know, act on, and watch for.
The Attack That Exposed AI’s Hidden Dependency Crisis
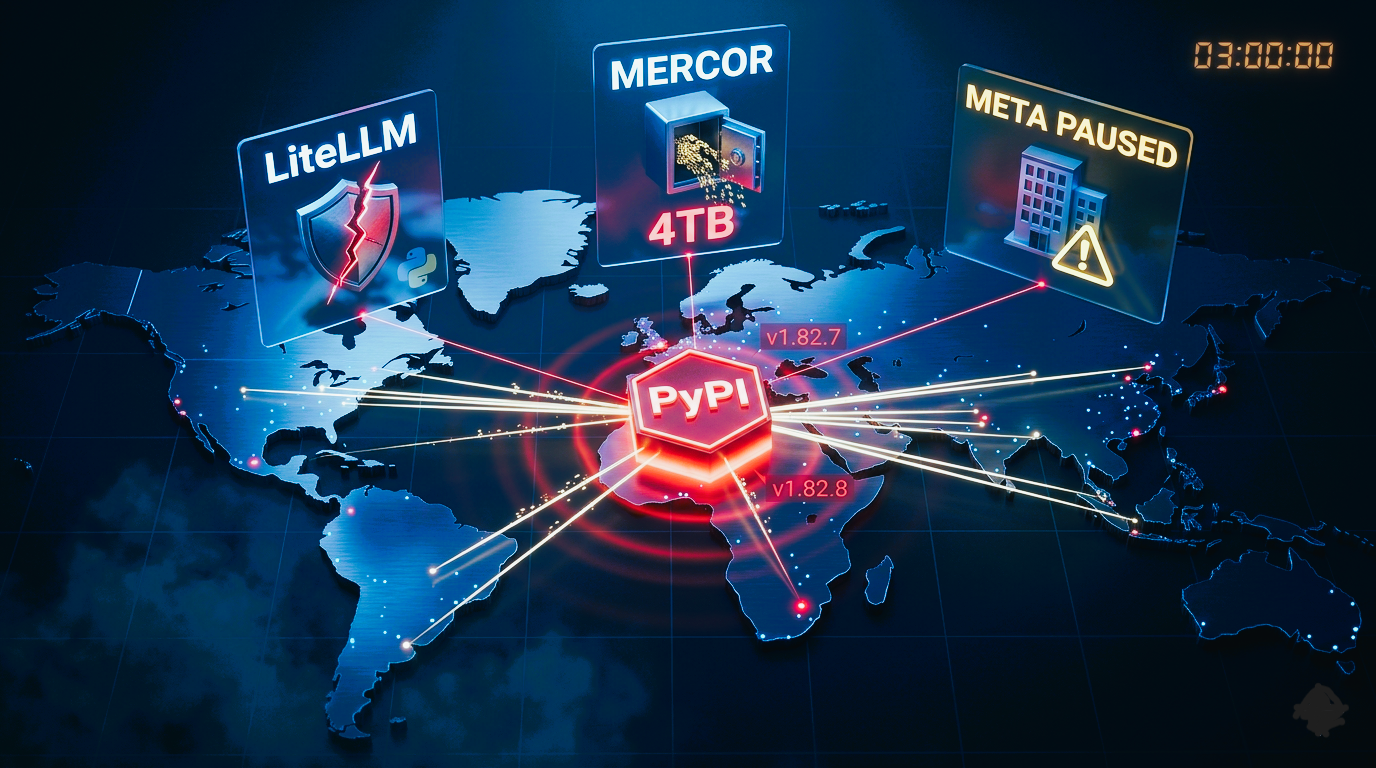
The malicious packages stayed live on PyPI for roughly three hours. That was enough. When TeamPCP a sophisticated multi-ecosystem threat actor pushed backdoored versions of LiteLLM (v1.82.7 and v1.82.8) onto the Python Package Index in late March 2026, they didn’t need days or weeks of access. Thousands of AI pipelines automated, hungry for the latest dependencies, running in CI/CD environments across the globe pulled those packages and executed their payload before most security teams had their morning coffee.
The downstream fallout has been extraordinary. Mercor, a $10 billion AI recruiting and annotation startup whose clients include OpenAI, Anthropic, and Meta, confirmed it was breached via the LiteLLM compromise becoming the first organization to publicly acknowledge being victimized through the TeamPCP campaign. The extortion group Lapsus$ claims to have walked away with 4TB of data: 939GB of source code, a 211GB user database, and roughly 3TB of video interviews and passport-scan identity documents from Mercor’s contractor network. Meta has since paused its work with Mercor while it investigates.
This article gives you the definitive account of what happened, how it happened, and most critically what you need to do about it. You’ll get the full Trivy-to-Mercor attack chain, a forensic breakdown of the malicious payload, a five-step incident response playbook, a vendor assessment checklist, and a risk framework for every component in your AI stack. Whether you’re a DevSecOps engineer auditing dependencies, a CISO briefing your board, or a founder deciding how much to trust third-party AI tooling, this is the resource you’ll send to your team.
⚠ Immediate Action Required
If your organization uses LiteLLM, check your dependency manifests now for versions v1.82.7 or v1.82.8. Even if you didn’t install these versions directly, CI/CD environments that ran during the exposure window may have pulled them transitively. See Section 5 for the full response playbook.
The Attack Chain: From Trivy to 4TB in Nine Days
To understand the Mercor LiteLLM supply chain breach, you need to go upstream. LiteLLM didn’t fail on its own. It was the third domino in a carefully engineered cascade that started with a security tool, of all things.
Phoenix Security’s forensic analysis of the TeamPCP campaign shows that the attack almost certainly began when a compromised Trivy CI/CD action ran inside LiteLLM’s own build pipeline. Trivy is a widely used open-source vulnerability scanner the kind of tool organizations add to their pipelines specifically to improve security. When the compromised action ran, it harvested LiteLLM’s PyPI publishing token. TeamPCP then used that token to push malicious releases directly to PyPI, bypassing GitHub’s version history entirely. No one outside the project’s maintainers would have seen the change coming.
// Attack Timeline: Trivy → LiteLLM → Mercor
1
~Mar 19-22, 2026
Trivy CI/CD Credential Theft
TeamPCP compromises a Trivy GitHub Action. When it runs in LiteLLM’s pipeline, it exfiltrates the PyPI publishing token. The project is unaware.
2
Mar 23, 2026
Malicious LiteLLM Releases Pushed to PyPI
TeamPCP publishes v1.82.7 and v1.82.8 to PyPI. Packages contain a three-stage credential harvesting payload embedded via a .pth auto-execution file. They remain live for approximately three hours before quarantine.
3
Mar 23-29, 2026
Thousands of AI Pipelines Pull Infected Packages
Automated CI/CD jobs and development environments at enterprises, AI labs, and AI startups worldwide pull the malicious versions. Credential theft begins immediately on package installation. The campaign targets at least five ecosystems: PyPI, npm, Docker Hub, GitHub Actions, and OpenVSX.
4
Late Mar 2026
Mercor Network Compromised via Tailscale VPN Credentials
Following LiteLLM-driven credential theft, attackers reportedly use a compromised Tailscale VPN credential for initial access to Mercor’s infrastructure. Lateral movement and data staging begin.
Mercor publicly discloses the incident, calling itself “one of thousands of companies” affected. SANS ISC designates Mercor as the first officially confirmed victim of the TeamPCP campaign.
6
Apr 3-4, 2026
Meta Pauses Work with Mercor
Business Insider confirms Meta has paused its AI training relationship with Mercor while it investigates exposure. The commercial fallout begins for a company valued just months earlier at $10 billion.
Trend Micro’s research team describes this as one of the most sophisticated multi-ecosystem supply chain campaigns publicly documented to date. The key insight that separates this campaign from run-of-the-mill package typosquatting: attackers didn’t create a fake LiteLLM package. They published to the real one, using legitimate credentials, making automated trust checks essentially useless.
Inside the Payload: What the Malicious LiteLLM Actually Did
The malicious LiteLLM package didn’t run obvious, easily-flagged code. It used a .pth file a Python path configuration mechanism that auto-executes on interpreter startup to ensure the payload ran any time Python initialized in the infected environment. You didn’t have to import LiteLLM. Installing it was enough.
The payload searched for and exfiltrated over 50 categories of secrets SSH keys, AWS and GCP access tokens, Kubernetes secrets, crypto wallet keys, .env files, and API credentials for LLM providers like OpenAI, Anthropic, and Cohere. For AI companies, these aren’t peripheral credentials. They’re the keys to the entire model inference and training infrastructure.
02
Stage 2: Kubernetes Lateral Movement
If a Kubernetes environment was detected, the payload attempted to deploy privileged pods to every node in the cluster. This isn’t just credential theft it’s a full cluster takeover bid, giving attackers the ability to observe, intercept, or modify workloads across the entire AI compute environment. Training jobs, inference services, data pipelines: all exposed.
03
Stage 3: Persistent Systemd Backdoor
Finally, the payload installed a systemd backdoor service that polled attacker-controlled infrastructure for additional binaries. Even if you removed the malicious package, the backdoor could persist and continue receiving new payloads until explicitly hunted and eradicated. Uninstalling LiteLLM and moving on is not a remediation strategy.
“Once triggered, the payload runs a three-stage attack: it harvests credentials (SSH keys, cloud tokens, Kubernetes secrets, crypto wallets, and .env files), attempts lateral movement across Kubernetes clusters by deploying privileged pods to every node, and installs a persistent systemd backdoor that polls for additional binaries.”
Endor Labs researcher, quoted in BleepingComputer, March 23, 2026
The .pth execution mechanism deserves special attention. Security teams focused on import-time analysis, runtime behavior detection, or network egress monitoring at the application layer may miss a payload that fires at the Python interpreter level before any application code runs. This is precisely why standard dependency auditing checking version numbers and known CVEs isn’t sufficient for AI supply chain risk.
Why the Mercor Breach Hits Differently
Every major supply chain breach is serious. This one is in a different category. Here’s why.
LiteLLM Is Everywhere in AI Infrastructure
LiteLLM isn’t a niche tool. It’s a unified interface that routes to over 100 LLM provider APIs OpenAI, Anthropic, Cohere, Mistral, Bedrock, Vertex, and dozens more. It’s used in AI agent frameworks, MCP servers, orchestration tools, and model evaluation pipelines across the industry. It has tens of thousands of GitHub stars and deep integration in precisely the kind of AI-adjacent tooling that organizations adopt quickly and audit slowly. Compromising LiteLLM is like compromising a universal key that fits every door in the AI infrastructure building.
Mercor’s Client List Is a Who’s Who of Frontier AI
Mercor doesn’t just work with any companies. Its clients reportedly include OpenAI, Anthropic, and Meta the organizations training the most powerful and commercially significant AI systems in the world. Mercor provides these clients with recruiting services, contractor management, data annotation, and AI training support. That means the company’s systems potentially touch training data, annotation workflows, and contractor identity information for frontier AI development. Even if no model weights were exfiltrated, the blast radius calculation changes entirely when this is your vendor’s client list.
The Data You Can’t Rotate
Most breach responses follow a standard playbook: rotate credentials, update keys, patch the vulnerability. The Mercor breach adds a dimension that playbook doesn’t cover well.
“The most alarming part of the Mercor breach isn’t just the source code theft it’s the biometric and identity data that can’t be rotated. You can change a password or an API key; you can’t change your face or the passport video you used to onboard to a training platform.”
IQ Source, “Mercor Breach: 4 TB of Biometric Data You Can’t Rotate,” March 31, 2026
Of the alleged 4TB exfiltrated, approximately 3TB consists of video interviews and passport-scan identity documents collected as part of Mercor’s contractor onboarding process. These documents belong to the thousands of contractors data annotators, AI trainers, evaluators who completed identity verification to work on AI training projects for top-tier labs. You can’t issue new passports. You can’t re-record someone’s face. The long-tail privacy risk from this data persists for years, and the fraud potential compounds every time it moves through threat-actor markets.
// Alleged Exfiltrated Data Breakdown (Lapsus$ Claim)
939 GB source code · 211 GB user database · ~3 TB video interviews & identity documents (passports). Total: ~4 TB. Note: Volumes are attacker-reported. Mercor has confirmed a significant breach but has not publicly validated specific size figures. Source: SANS ISC, March 31, 2026.
The commercial fallout is already moving faster than the forensics. Meta has paused its work with Mercor. A $10 billion company built on trust trust from contractors sharing their identities, trust from AI labs sharing their workflows now has both eroded simultaneously. As Kenneth Hartman of SANS ISC noted in the campaign’s Update 005 diary, Mercor “has publicly confirmed it was breached as a direct consequence of the LiteLLM supply chain compromise, making it the first organization to officially acknowledge being victimized through the TeamPCP campaign.” That phrase “first organization” should be read as a warning: it won’t be the last.
Incident Response Playbook for Affected Organizations
If your organization uses LiteLLM directly, or via any AI framework that depends on it here is the structured response sequence. Don’t treat this as a “check if we installed the bad version” exercise. Given the three-stage payload and persistent backdoor, the scope of required remediation is considerably larger.
01
Confirm Exposure Window (0-24 Hours)
Determine whether any system, container, or CI/CD job installed litellm==1.82.7 or litellm==1.82.8 during the malicious window. Check your SBOM tooling, pip install logs, lockfiles (requirements.txt, poetry.lock, Pipfile.lock), container image manifests, and build logs. Also check for the malicious C2 domains published by Phoenix Security and Trend Micro in your egress logs. Don’t assume only direct dependencies matter transitive installs and CI environments are primary exposure vectors.
02
Rotate All Potentially Exposed Credentials (24-72 Hours)
The payload targeted over 50 secret types. Rotate aggressively: cloud provider access keys (AWS, GCP, Azure), LLM provider API keys, Kubernetes secrets and service account tokens, SSH keys on any host that ran the package, .env-file contents, CI/CD pipeline secrets, and crypto wallet keys. Don’t wait for forensics to confirm compromise before rotating. Assume compromise and rotate then verify.
Monitor for usage of old credentials after rotation. Continuing usage after revocation confirms active attacker access.
03
Hunt for Persistence and Lateral Movement (1-2 Weeks)
This is the step most organizations skip and then regret. Use published IOCs from Trend Micro, Phoenix, and Endor Labs to systematically search for: unexpected systemd services installed after the exposure window; anomalous Kubernetes pods in your clusters (especially privileged or DaemonSet-style deployments you didn’t create); outbound connections to unknown infrastructure; and signs of credential replay from unexpected IPs or regions.
Treating this as a package-uninstall problem will leave you with a persistent backdoor.
04
Assess Your AI Vendor Exposure (1-4 Weeks)
If you use AI data vendors, annotation providers, or training services especially any that use LiteLLM or similar AI gateway libraries contact them now. Request their incident response statement specific to the LiteLLM compromise, ask for their current SBOM for key services, and verify what Tailscale or VPN credential controls they have in place. The Mercor case demonstrates that vendor compromise can expose your contractors’ identities, your training workflows, and your annotated data not just the vendor’s own systems.
05
Regulatory and Legal Response (Ongoing)
If any of your contractors’ or users’ identity documents, biometric data, or personal information may have been exposed via a vendor like Mercor, engage your data protection officer and privacy counsel immediately. Biometric data carries special classification under GDPR Article 9, CCPA, and numerous state-level biometric privacy laws (BIPA in Illinois, for example). Notification obligations may be triggered; delays compound regulatory exposure. The “non-rotatable” nature of biometric data makes the individual harm calculation more severe, which regulators are increasingly factoring into enforcement decisions.
AI Vendor Supply Chain Risk Checklist
Send this to your AI data vendors, annotation providers, orchestration tool vendors, and any third-party touching your model pipelines. The Mercor breach didn’t happen in a vacuum it happened because security questionnaires for AI vendors haven’t caught up to AI vendors’ actual attack surface.
// Vendor Security Assessment: AI Supply Chain (Post-LiteLLM)
Do you use LiteLLM, LangChain, or similar AI gateway libraries in your production infrastructure? If yes, which versions are deployed, and what remediation steps did you take after March 24, 2026?
Provide a current Software Bill of Materials (SBOM) for your key services, including transitive Python and JavaScript dependencies used in AI orchestration, annotation, or inference pipelines.
How are your PyPI, npm, and container registry publishing credentials managed? Are they stored in CI/CD systems, and how are they isolated from the workloads that consume those packages?
What controls prevent a compromised third-party CI/CD action (e.g., a GitHub Action like Trivy) from exfiltrating secrets used in your own publishing pipeline?
Describe your secret-management approach are secrets stored in a dedicated KMS (AWS Secrets Manager, HashiCorp Vault, GCP Secret Manager), what are your rotation policies, and do you run automated scanning for hard-coded secrets in repos and container images?
What logging and telemetry do you maintain for package installation events, and do you alert on anomalous outbound connections from build and inference environments?
What are your Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR) benchmarks for a supply chain compromise event? Have you exercised this scenario in a tabletop or red team exercise in the past 12 months?
For data labeling, annotation, and recruiting vendors: how are contractor biometric data, identity documents, and video recordings stored? Are they encrypted at rest with customer-managed keys? Who has access, and what retention and deletion policies govern them?
What contractual commitments indemnification clauses, SLA penalties, incident notification timelines apply if your supply chain results in exfiltration of our data or our contractors’ personal information?
Have you retained a third-party forensics firm to investigate the LiteLLM exposure window? When do you expect to provide a final incident report?
Where AI Supply Chains Break: Risk Hotspots Across the Stack
The LiteLLM campaign didn’t just compromise one tool. It exposed a structural problem: AI infrastructure is built on a dense, poorly-audited web of dependencies, each of which can serve as an entry point. Here’s how the risk breaks down across the key components in a typical AI stack.
Stack Component
Example Tools
Credential Risk
Data Exfil Risk
IP Leakage Risk
Compliance Risk
AI Gateway / Proxy
LiteLLM, OpenRouter
HIGH
HIGH
HIGH
HIGH
CI/CD Actions
Trivy, GitHub Actions
HIGH
MED
MED
LOW
Annotation / Labeling Vendor
Mercor, Scale AI
MED
HIGH
HIGH
HIGH
Orchestration Framework
LangChain, CrewAI
HIGH
MED
MED
MED
Evaluation Tooling
Evals frameworks, RLHF tooling
LOW
MED
MED
LOW
Container / Image Registry
Docker Hub, GHCR
HIGH
MED
HIGH
LOW
Cloud Infra (K8s / Serverless)
EKS, GKE, Lambda
MED
HIGH
HIGH
MED
The table makes one thing clear: AI gateways like LiteLLM are the highest-risk single point in the stack because they concentrate API keys and cloud credentials for every LLM provider in use. As Trend Micro Research observed, “AI proxy services that concentrate API keys and cloud credentials become high-value collateral when supply chain attacks compromise upstream dependencies.” One compromised gateway = every model provider credential, simultaneously.
The Contrarian View: Don’t Panic, But Don’t Look Away
The temptation after an incident like this is to swing hard in the other direction ban open-source AI tooling, rebuild everything in-house, treat every PyPI package as hostile. That reaction creates as much risk as it mitigates.
The problem isn’t that LiteLLM is open-source. Open-source software’s transparency is genuinely a security asset over time: vulnerabilities get found, discussed, and fixed in the open. The problem is organizational: most teams that adopted LiteLLM did so with the same diligence they’d apply to a SaaS subscription, not a critical infrastructure dependency. That mismatch between deployment speed and security rigor is where the breach lives, and rebuilding in-house doesn’t fix it it just changes which codebase you fail to audit.
What does help:
Treat AI dependencies as critical infrastructure. Organizations that require SBOMs, pin dependencies, and review transitive package graphs for database connectors should do the same for AI libraries. The blast radius of a compromised AI gateway dwarfs most database vulnerabilities.
Minimize the secrets your AI tools can see. LiteLLM’s credential exposure was so severe because many deployments gave it access to all LLM provider keys simultaneously exactly the design it enables. Scope credentials tightly. Use separate keys per provider, rotate them on short cycles, and consider whether your AI gateway needs to run with the same permissions as your cloud control plane.
Design for resilience, not just prevention.Phoenix Security’s analysis notes that the malicious packages were live for only about three hours. Good tooling didn’t prevent that window but organizations with strong egress monitoring, anomaly detection, and fast credential revocation workflows would have contained the damage significantly. Prevention is insufficient. Assume compromise and build resilient response.
// The Realistic Timeline
Vendor narrative: “We’ve patched the package and rotated keys risk is contained.” | Reality: Full credential rotation, backdoor eradication, vendor assurance, regulatory notification, and insurance claims will span weeks to months across most AI-heavy organizations. Early-stage companies without mature IR practices face even longer timelines, and some will never fully close their exposure windows.
Frequently Asked Questions
The Mercor LiteLLM supply chain breach is a 2026 security incident in which threat actor TeamPCP compromised the open-source LiteLLM library on PyPI, embedding a credential-stealing payload. AI recruiting and annotation startup Mercor serving clients including OpenAI, Anthropic, and Meta confirmed it was breached via this compromise, with extortion group Lapsus$ claiming to have exfiltrated approximately 4TB of sensitive data including source code, user databases, and identity documents. TechCrunch coverage →
TeamPCP almost certainly stole LiteLLM’s PyPI publishing token by running a compromised Trivy CI/CD action inside LiteLLM’s own build pipeline. Using that token, they published malicious versions 1.82.7 and 1.82.8 directly to PyPI bypassing GitHub’s version history with a three-stage payload embedded via a .pth auto-execution file. The packages remained live for approximately three hours before quarantine, but that window was enough to reach thousands of environments. Phoenix Security analysis →
According to attacker claims corroborated by SANS ISC and multiple security analyses, the alleged exfiltration includes approximately 939GB of source code, a 211GB user database, and roughly 3TB of video interviews and passport-style identity verification documents collected during contractor onboarding. The biometric and identity components are particularly serious because they cannot be “rotated” the way credentials can. Note that Mercor has confirmed a significant breach but has not publicly validated specific volume figures. SANS ISC Update 005 →
Mercor has publicly confirmed being breached and describes itself as one of thousands of organizations affected. Any organization that installed LiteLLM v1.82.7 or v1.82.8 during the exposure window may have had credentials harvested. Mercor’s clients reportedly include OpenAI, Anthropic, and Meta, though no evidence has been published that those companies’ own systems or training data were directly accessed. Meta has paused its work with Mercor while investigating. Business Insider coverage →
Scan your SBOM tooling, dependency manifests, pip install logs, and container image layers for LiteLLM versions 1.82.7 or 1.82.8. Review your network egress logs against the C2 domains published by Trend Micro, Phoenix Security, and Endor Labs. Check for unexpected systemd services or Kubernetes pods deployed around the exposure window (approximately March 23, 2026). Also audit CI/CD build logs the package may have been installed transiently in a build environment even if it’s not in production dependencies. Upwind Security guide →
Three compounding factors. First, Mercor’s clients include frontier AI labs, meaning the blast radius touches the most commercially sensitive AI training and annotation workflows in the industry. Second, the exfiltrated data includes biometric and identity documents that cannot be remediated the way credentials can affected contractors face permanent, long-tail fraud and privacy risk. Third, the incident demonstrates that AI infrastructure’s rapid growth has created a class of high-value targets AI gateways, annotation platforms, evaluation tooling that the security industry hasn’t yet developed robust governance frameworks for. IQ Source analysis →
In priority order: (1) Identify all systems that installed LiteLLM v1.82.7 or v1.82.8. (2) Rotate all credentials on affected hosts cloud tokens, API keys, SSH keys, Kubernetes secrets. (3) Hunt for the persistent systemd backdoor and anomalous Kubernetes pods using published IOCs. (4) Contact AI-related vendors to assess their LiteLLM exposure and remediation. (5) Engage legal and privacy counsel if any personal or biometric data may have been involved. See the full five-step playbook in Section 5. Full breakdown →
Most security experts say no. The problem isn’t open-source AI tooling it’s the gap between adoption velocity and security governance. The right response is treating AI dependencies as critical infrastructure: requiring SBOMs, pinning versions, monitoring installs, scoping credential access tightly, and maintaining egress visibility. Wholesale abandonment of open-source AI tooling in favor of rushed in-house rebuilds creates different, often larger risks. Upwind Security →
In the short term: vendor pauses, security reviews, and stricter contract terms are already happening (see Meta’s pause on Mercor). In the medium term: expect accelerated investment in AI-supply-chain security tooling, SBOM requirements in procurement, and more rigorous vendor due diligence frameworks. In the long term: this breach may prove a positive forcing function the kind of high-profile incident that finally drives AI teams to adopt the supply-chain governance practices that software-at-large learned from SolarWinds and Log4Shell. Market context →
What Comes Next
The Mercor LiteLLM supply chain breach reveals something the AI industry has managed to avoid confronting at scale until now: the attack surface of modern AI infrastructure isn’t primarily the models. It’s the dense, fast-moving, poorly-governed dependency graph underneath them. TeamPCP didn’t need to crack a foundation model or defeat an alignment system. They compromised a CI/CD scanner, stole a publishing token, and waited three hours. The rest was automated.
The structural lesson isn’t unique to AI it’s the same lesson the software industry learned from SolarWinds in 2020 and Log4Shell in 2021. But AI’s particular characteristics make it acutely vulnerable: adoption velocity that outruns security governance, deep integration of credential-rich gateway tools, and a category of data biometrics, identity documents, annotated training material that carries long-tail risk well beyond what typical credential rotations can address.
Three developments are worth watching in the months ahead. First: whether Mercor is truly “one of thousands” or the first of many public disclosures, as affected organizations complete forensic investigations and face disclosure timelines. Second: whether the AI developer tools market sees a consolidation or bifurcation between providers who can demonstrate security maturity via SBOMs, audits, and incident-response track records, and those who can’t. Third: whether regulators particularly those with jurisdiction over biometric data use the Mercor breach to accelerate enforcement action that establishes precedent for how AI training vendors must protect contractor identity data.
The Mercor LiteLLM supply chain breach is not the last attack of its kind. It’s the proof-of-concept that made the playbook obvious. Organizations that build AI supply chain governance now before the next campaign, before the regulation, before the next Meta-style contract pause will be the ones that don’t have to write that breach disclosure.
Disclaimer: This article is an editorial analysis compiled from publicly available security research, news reporting, and attacker claims. Volume and data figures attributed to Lapsus$ are unverified attacker claims; Mercor has confirmed a significant breach but has not publicly validated specific data volumes. NeuralWired is not a cybersecurity firm and this analysis does not constitute legal, compliance, or incident response advice. Consult qualified security and legal professionals for decisions affecting your organization.
Trump’s 2026 Cyber Strategy: Offense First, Details Later | NeuralWiredNeuralWired
Deep analysis for frontier technology professionals
National Security · Cybersecurity Policy
Trump’s Cyber Strategy: Offense First, Details Later
A 7-page doctrine pivoting the US to aggressive, AI-powered cyber operations, released the same day China allegedly walked out of the FBI’s network.
NeuralWired Staff|March 7, 2026|~ · 10 min read
On March 6, 2026, the White House published its long-awaited national cyber strategy. That same day, the Wall Street Journal reported that suspected Chinese state hackers had breached an FBI surveillance network, detected weeks earlier on February 17. The juxtaposition was hard to miss.
Whether coincidental or orchestrated, the timing underscored the document’s central argument: the US has spent years playing defense, and it’s losing. The Trump administration’s answer is a seven-page strategy built around six pillars, the most prominent of which is a push toward offensive cyber operations and the explicit “unleashing” of the private sector to join in.
The strategy and a companion executive order on cybercrime dropped within hours of each other. For CISOs, CTOs, and enterprise security teams, the combined package represents a meaningful shift in the US threat posture, though exactly how meaningful depends on implementation details that don’t yet exist.
6Policy pillars in the strategy
$15BStolen funds seized from scammers (cited in strategy)
$12.5BUS fraud losses in 2024 per FTC data
Feb 17Date FBI detected abnormal network activity
The Six Pillars: What’s Actually New
The strategy document organizes US cyber priorities into six areas. What’s notable isn’t just which pillars appear. It’s the ordering and emphasis.
01
Deter & Defeat Adversaries
Offensive operations against hostile actors; private sector incentives to disrupt threat networks.
02
Strengthen Federal Networks
Zero-trust architecture mandates and post-quantum encryption across government systems.
03
Protect Critical Infrastructure
Energy, finance, and data centers; partnership with sector-specific agencies.
04
Combat Cybercrime & Fraud
DOJ/State coordination on sanctions; dismantling fraud networks targeting US citizens.
05
Achieve Tech Superiority
AI supply chains, semiconductor security, agentic AI tools for defense.
06
Build the Cyber Workforce
Federal talent pipelines and private-sector alignment on security skills.
Prior administrations typically buried deterrence language deep in strategy documents, treating it as a diplomatic afterthought. This one leads with it. CSO Online noted the explicit elevation immediately.
“By moving the usual ‘deterrence’ part to the top and focusing on offense, which is usually only lightly referred to in past unclassified strategies, the administration has greatly emphasized that pillar.”
Ari Schwartz, Managing Director, Cybersecurity Services & Policy, Venable LLP; former White House cybersecurity director
Schwartz’s read matters because he has worked across multiple administrations and understands the difference between rhetorical posturing and doctrinal change. Putting offense first in an unclassified strategy sends a signal to adversaries, allies, and the private sector: the default posture is no longer “detect and respond.” It’s “find and disrupt.”
The same day the strategy published, the WSJ reported that Chinese state-affiliated hackers had compromised an FBI surveillance network holding domestic monitoring data. The FBI had detected abnormal log activity on February 17; Congress was notified in the days before the story broke.
White House releases 7-page “Cyber Strategy for America” and companion executive order on cybercrime and fraud.
March 6, 2026
WSJ reports suspected Chinese state actors behind FBI breach. NSA and CISA join FBI in remediation.
March 7, 2026 (ongoing)
Agencies actively remediating breach; scope and full severity still being assessed.
The breach remains at an early investigative stage. Reuters confirmed the hack was described as sophisticated, but the full scope is unknown. NSA and CISA are assisting the FBI. Critically, the compromised system was unclassified, which means procedures designed to protect classified networks weren’t the attack surface here.
For enterprise security teams, that’s the uncomfortable lesson: classified-tier controls can coexist with a breach of workaday, unclassified infrastructure. The FBI’s surveillance network contained data on domestic monitoring orders. Sensitive, not formally classified. That gap between “sensitive” and “classified” is exactly where adversaries operate.
The strategy’s Pillar 1, focused on deterring adversaries through offensive pressure and private-sector disruption, is directly relevant here. If the doctrine had been operational, the question isn’t just “how did China get in?” but “what proactive steps could have disrupted the operation before February 17?”
The AI and Technology Superiority Pillar: What CISOs Actually Need to Do
Pillar 5 is where the strategy intersects most concretely with enterprise security budgets. The document mandates attention to AI supply chains, semiconductor provenance, and the deployment of agentic AI tools for cyber defense. The language is high-level. This is a strategy document, not a technical specification. But the direction is clear.
Per the analysis from CSO Online, the strategy calls for secure AI stacks and data centers as a national security matter, not just a commercial preference. That has procurement implications for any enterprise with federal contracts or critical infrastructure designations.
The deregulation emphasis runs through the technology pillar. The administration argues that regulatory overhead has slowed AI innovation in the security domain, giving adversaries room to advance. Whether that argument holds is debatable. Several security researchers have noted that lax regulation is also how vulnerabilities proliferate. Expect procurement and compliance teams to get questions about it from leadership.
The zero-trust and post-quantum requirements in Pillar 2 apply specifically to federal networks, but they function as de facto standards for any organization doing business with the federal government. If your network connects to a federal agency’s network, their zero-trust posture becomes your concern.
The Fraud Executive Order: A Separate But Connected Track
The companion executive order on cybercrime and fraud operates on a different track from the national security pillars, but the two documents reinforce each other.
The EO directs DOJ and the State Department to coordinate sanctions against jurisdictions that harbor fraud operations and to develop mechanisms for returning seized funds to victims. The administration cited FTC data showing $12.5 billion in US fraud losses during 2024, a figure that represented 38% of fraud reports resulting in financial loss, up from 27% the prior year. The strategy also cited $15 billion in stolen funds already seized under previous Trump administration operations.
For financial institutions and payment processors, the EO signals increased federal coordination on fraud networks, which means more information sharing requests, more potential for joint operations, and more compliance touchpoints. For investors in cybersecurity companies focused on fraud detection, the policy tailwind is meaningful.
What’s Missing, and Why That Matters
The strategy’s critics are not wrong. Seven pages is light for a document meant to govern US cyber posture across the federal government, critical infrastructure, and private sector. Cybersecurity Dive flagged the gap between the document’s ambitious rhetoric and its thin implementation details. IST experts offered a pointed assessment of the infrastructure pillar specifically.
“The 2026 Cyber Strategy includes critical infrastructure security, but falls short on the specific support” for state, local, tribal, and territorial governments.
Institute for Security and Technology (IST) Expert Analysis, March 2026
The SLTT gap is significant. Critical infrastructure (water treatment plants, local power grids, small municipal systems) is overwhelmingly operated by entities that lack federal resources and often lack dedicated security staff. A national strategy that focuses on offensive capabilities and federal network hardening without a corresponding plan for SLTT support leaves the most vulnerable nodes exposed.
The administration has indicated that follow-on implementation plans are imminent. Watch for agency-level action plans in Q2 2026 that will fill in operational details. The strategy document is a declaration of direction; the action plans will determine whether it’s achievable.
The CISO Playbook: Translating 6 Pillars Into Action
The coverage gap across every competitor who’s covered this story is the same: they describe the pillars but don’t translate them. Here’s what each pillar actually demands from enterprise security teams right now.
Pillar 1 (Offense/Deterrence): Review your threat intelligence partnerships and ISACs. Understand what “private sector incentives to disrupt adversary networks” means for your legal exposure before your vendor pitches you on offensive tools.
Pillar 2 (Federal Networks): If you have federal contracts, audit your zero-trust maturity against NIST SP 800-207. Post-quantum migration timelines are no longer theoretical. Begin inventory of cryptographic dependencies.
Pillar 3 (Critical Infrastructure): Energy, finance, healthcare, and data center operators: expect tightened sector-specific requirements in Q2-Q3 2026. Map your current controls to CISA frameworks now.
Pillar 4 (Cybercrime/Fraud): Financial institutions should anticipate increased federal coordination requests on fraud networks. Review information-sharing agreements and ensure your legal team understands the EO’s victim-fund return mechanisms.
Pillar 5 (AI/Tech Superiority): Conduct an AI supply chain audit. Identify any AI tools or model providers with provenance questions. Chinese-origin AI components in federal-adjacent infrastructure will draw scrutiny.
Pillar 6 (Workforce): The talent gap the strategy acknowledges is real. Review compensation benchmarks for security roles. Federal competition for talent will intensify.
The pattern here is legible even before the implementation details arrive: the US is shifting from a fundamentally reactive cyber posture to a proactive one, and it’s betting that offensive deterrence, combined with AI-enabled defense, is more effective than the decade-long experiment in graduated response and international norm-building.
That bet carries real risks. Escalation dynamics in cyberspace are not well-modeled. The FBI breach, allegedly Chinese-linked, arriving simultaneously with a strategy that promises more aggressive retaliation raises the obvious question of sequencing: is this a response to China’s behavior, or will it provoke more of it? The answer is probably both, which is the uncomfortable arithmetic at the center of any offensive doctrine.
Watch for three developments in the next 90 days: (1) agency-level implementation plans that will reveal whether the strategy has operational teeth or remains aspirational, (2) the full scope of the FBI breach assessment, which will test whether Pillar 1 gets resourced in proportion to the threat it’s meant to address, and (3) the first private-sector partnership announcements under the offensive operations pillar, which will define exactly what “unleashing” the private sector means in practice. The organizations and CISOs that align their security postures now, before those details land, will have less catching up to do when implementation moves from strategy to mandate.