Walmart Cut Food Tracing From 7 Days to 2.2 Seconds. Why Is Your Supply Chain Still Running on Excel? | NeuralWiredBlockchain • Enterprise Technology
Walmart Cut Food Tracing From 7 Days to 2.2 Seconds. Why Is Your Supply Chain Still Running on Excel?
By NeuralWired Research Desk • June 12, 2026 • 14 min read
Quick Answer
Blockchain supply chain management is a distributed ledger technology that creates a tamper-proof, real-time record of every transaction and movement across a supply chain. Walmart used it to reduce food traceability from 7 days to 2.2 seconds. Nestlé projects $47 million in savings over five years. The market hit $5.23 billion in 2026 and is heading to $21.29 billion by 2029. The risk isn’t whether blockchain works. It’s whether your governance model will.
In October 2016, Walmart handed IBM a mango. That’s the simplified version of what actually happened: Walmart partnered with IBM to run a blockchain pilot using Hyperledger Fabric to trace mangoes through its U.S. stores and pork through its Chinese supply chain. The goal was to answer a question that had haunted the food industry for decades: when something goes wrong, how fast can you find the source?
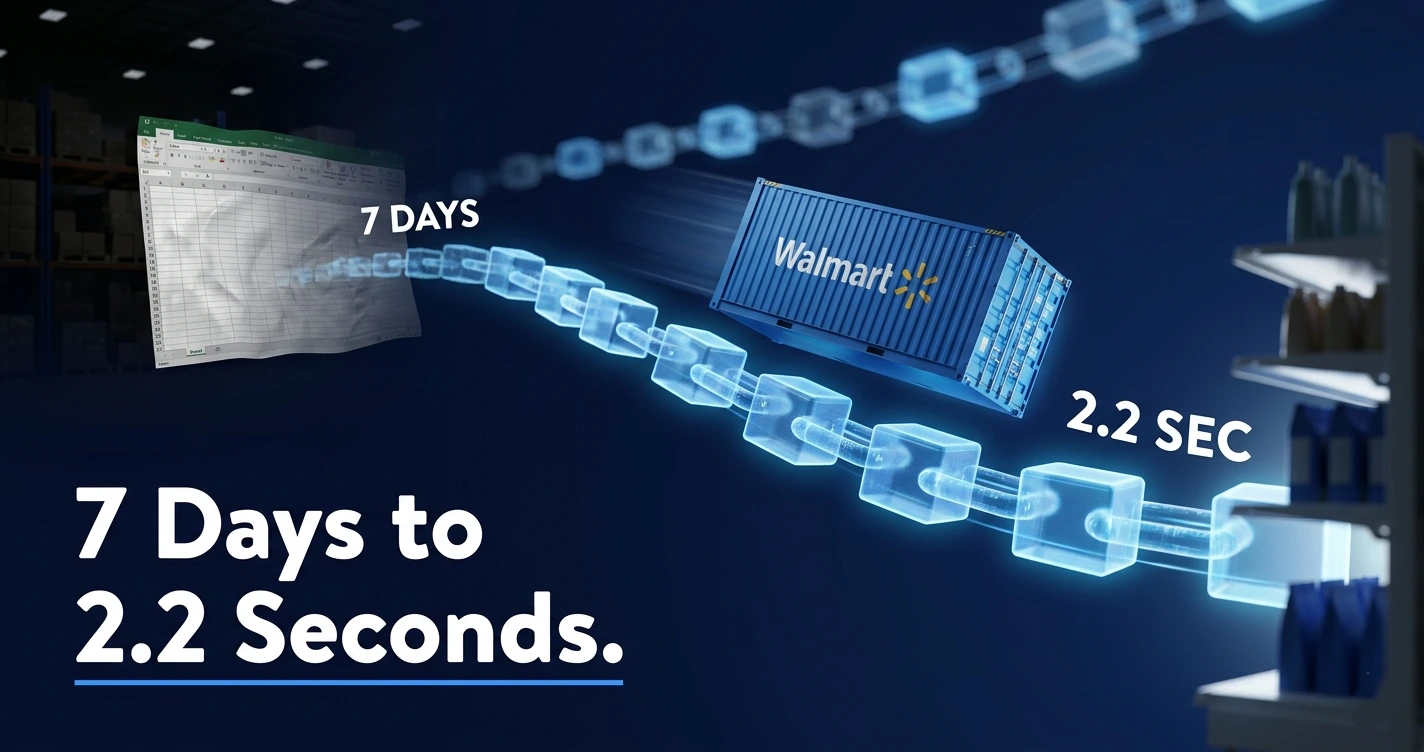
The answer, before blockchain supply chain management, was seven days. That’s how long it took to trace a contaminated item from store shelf back to farm origin. The answer after? 2.2 seconds. Frank Yiannas, then Walmart’s VP of Food Safety, confirmed that number publicly in 2018. It remains the single most cited performance benchmark in enterprise blockchain history.
This article exists at the intersection of those two facts. It’s written for CTOs, VP Supply Chain, and enterprise architects who are done with the hype cycle and want to know what blockchain in supply chain actually delivers, what it costs when it fails, and what you need to get right before you spend the first dollar.
Blockchain supply chain management is the application of distributed ledger technology to record, verify, and share supply chain data across multiple parties in real time. Each transaction, shipment, inspection, or payment is written as a block onto a chain that no single participant can alter retroactively. Every authorized party sees the same version of the data simultaneously.
The core problem it solves isn’t storage. It’s trust. In a traditional supply chain, a manufacturer trusts a distributor’s spreadsheet. A retailer trusts a supplier’s PDF. A regulator trusts a stack of documents that took 7 days to assemble. Blockchain replaces that chain of trust-me-on-this with a chain of cryptographically verified records. The data doesn’t travel by email. It lives on a shared ledger that updates in real time.
Smart contracts extend this further. These are self-executing programs written onto the blockchain that trigger automatically when conditions are met. A shipment clears customs and a payment fires instantly. A temperature threshold is breached in cold chain logistics and a rejection alert goes out without human intervention. In 2025, more than 65,000 smart contracts were executed across logistics and manufacturing use cases, according to the Blockchain Council.
Why this matters right now
In February 2025, U.S. Senators Maria Cantwell, Marsha Blackburn, and Lisa Blunt Rochester introduced S.257, a bipartisan bill requiring the Department of Commerce to analyze U.S. supply chain security using blockchain and AI. Blockchain isn’t waiting for the market to validate it. The regulatory clock has started.
The Proof It Works: Walmart, Nestlé, and the Numbers
The case for blockchain supply chain management isn’t theoretical. It’s documented, named, and sourced. Here’s what the data actually says.
2.2 sec
Time for Walmart to trace a food item from store to farm, after blockchain. Previously: 7 days.
Walmart and IBM Food Trust
The Walmart pilot began with mangoes and pork. By 2018, it had expanded to poultry, berries, yogurt, and leafy greens. Walmart mandated all leafy green suppliers join IBM Food Trust by September 2019. Suppliers who didn’t comply lost the business. IBM Food Trust grew to 188 organizations in its network. The 7-days-to-2.2-seconds traceability result remains uncontested in any published rebuttal.
Nestlé’s $47 Million Projection
Nestlé’s blockchain supply chain deployment projects $47 million in savings over five years, according to case study data compiled by Marketing Scoop. This covers traceability, waste reduction, and supplier audit efficiency. For an enterprise CTO evaluating ROI, this isn’t a pilot curiosity. It’s a named financial case from one of the world’s largest food manufacturers.
The Full ROI Picture
81%
Average drop in trade finance processing time with blockchain
33%
Reduction in operational costs across documented deployments
42%
Lower administrative costs via smart contract automation
82%
Executives reporting positive ROI within two years
These figures come from SQ Magazine’s December 2025 synthesis of 15+ industry studies. They’re not projections from a vendor pitch deck. They’re documented benchmarks from production deployments. If you’re on the fence about whether the economics work, the 82% two-year ROI confidence figure from surveyed executives is the most straightforward answer available.
“Supply chain is no longer a back-office function. It’s central to business, bringing resilience and value in equal measure.”
Simon Bailey, VP Analyst, Supply Chain Practice, Gartner — June 2025
In 2025, trade finance platforms running on blockchain processed $24.7 billion in transaction volumes. The market doesn’t care what your spreadsheet says about the maturity of this technology. It’s processing $24.7 billion and growing.
Maersk TradeLens: What the $21.29B Market Doesn’t Tell You
Every honest article about blockchain supply chain management has to spend time here. Because TradeLens is the most important story in enterprise technology that most CTOs still misread.
In 2014, Maersk started exploring blockchain for global trade. By 2018, TradeLens was live: a permissioned blockchain network jointly built by Maersk (51%) and IBM (49%), headquartered in New York. By 2022, it was tracking 67 million containers, had processed over 3.5 billion shipping events, and had onboarded more than 150 organizations, including CMA CGM and Mediterranean Shipping Company.
It also delivered documented results. TradeLens claimed a 20% reduction in documentation costs and a 40% reduction in shipment time. The traditional shipping baseline it improved on was a 34-day transit timeline, with 14 days wasted solely on customs paperwork, across 30-plus organizations per single shipment.
On November 29, 2022, Maersk shut it down.
“While we successfully developed a viable platform, the need for full global industry collaboration has not been achieved. As a result, TradeLens has not reached the level of commercial viability necessary to continue work and meet the financial expectations as an independent business.”
Rotem Hershko, Head of Business Platforms, Maersk — November 2022, via CoinTelegraph
Read that quote carefully. Hershko doesn’t say the technology failed. He says the collaboration failed. That distinction is everything.
The Academic Autopsy
In March 2025, researchers from HECF Business School published a peer-reviewed analysis in Frontiers in Blockchain applying Ostrom’s commons theory to TradeLens. Their conclusion: the platform failed because of commons governance failure, not technology failure.
The researchers identified the core structural problem: TradeLens was a shared digital commons built on competitive infrastructure. Maersk and IBM owned the network. Competitors were being asked to put their most sensitive logistics data into a platform run by their largest rival. The incentive structure was broken from day one. The technology tracked 67 million containers. The politics killed it.
This is the lesson every enterprise architect needs to internalize before they start any blockchain supply chain project. The governance question isn’t a secondary concern. It’s the primary risk factor. Who owns the network? Who resolves disputes? What happens when a key participant decides their competitive advantage outweighs the network benefit?
The Consortium Trap
You build a blockchain consortium for your sector. A key competitor refuses to join. The network effect never materializes. The investment becomes stranded infrastructure. TradeLens didn’t fail because Maersk built something that didn’t work. It failed because the shipping industry’s competitive dynamics were incompatible with shared ownership. Map your industry’s dynamics before you map your architecture.
For the record: Maersk hasn’t abandoned blockchain. Their Q4 2024 logistics trend map, based on a Statista survey of 500-plus global logistics decision-makers, still tracks blockchain as an active investment area. They’re just being more careful about governance this time.
Market Reality in 2026: Past Pilots, Into Production
The most important number in the blockchain supply chain story right now isn’t a ROI figure. It’s the year-over-year market growth from 2025 to 2026: $3.27 billion to $5.23 billion. That’s a 60% jump in 12 months, and it’s happening because production deployments are now outnumbering pilots.
Metric
Figure
Source
Market size (2026)
$5.23 billion
Blockchain Council, March 2026
Projected market (2029)
$21.29 billion at 59.8% CAGR
The Business Research Company
Cloud-hosted networks (market share)
60.72%
Mordor Intelligence, January 2026
Private blockchain enterprise share
54.22%
Blockchain Council, March 2026
Smart contracts executed (2025)
65,000+ in logistics and manufacturing
Blockchain Council, March 2026
Trade finance volume on blockchain (2025)
$24.7 billion
Blockchain Council, March 2026
Supply chain managers using Excel
67.4%
Adelante SCM Survey, via Supply Chain Dive
The Excel statistic isn’t rhetorical. It’s a real operational risk. Supply chain disruptions cause an average 62% financial loss according to ISM data, and the companies still running manual reconciliation across multiple spreadsheets are the most exposed. The visibility gap isn’t an inconvenience. It’s a liability.
“Remember that five or six years ago, blockchain was going to change the world.”
Mike Dominy, Analyst, Supply Chain Practice, Gartner — December 2024, via TechTarget
Dominy’s comment is worth sitting with. The hype was real. The disappointment was real. But his full statement adds the nuance: “There’s a greater degree of scrutiny by CFOs on digital investments in general and digital supply chain investments, but I don’t see any abandoning yet.” Scrutiny isn’t abandonment. It’s maturity.
Our read: the 2025-to-2026 numbers confirm that blockchain in supply chain has crossed from “are we doing this?” to “how are we doing this?” The CFO scrutiny Dominy describes is now producing better-scoped projects with cleaner ROI cases, not fewer projects.
The Architecture Decision Every CTO Has to Make
Before any blockchain supply chain project starts, one question determines everything else: private, consortium, or hybrid?
Private Blockchain (54% of enterprise deployments)
A private or permissioned blockchain is controlled by a single organization. It’s faster, cheaper per transaction, and keeps sensitive data out of shared infrastructure. This is the dominant model in 2026 for exactly those reasons. The trade-off: you lose the network effects that make blockchain valuable in multi-party workflows. If your goal is internal traceability and process automation, private is the right call. If your goal is cross-industry data sharing, you’ve built an island.
Consortium Blockchain (Shared Governance)
Multiple organizations jointly govern the network. This is the TradeLens model, and the governance risk is real. But done correctly, with neutral stewardship and clear shared incentives, consortium blockchain delivers the full network effect. The Trust Your Supplier platform (supplier onboarding) and IBM Food Trust (188 organizations) both run consortium models that have survived because the governance was built before the technology was deployed.
Hybrid Architecture (The 2026 Answer)
Private for sensitive internal data. Consortium or public for external verification. This is the emerging standard in 2026 deployments: keep your pricing and supplier contracts on a private chain, publish provenance and compliance data to a shared ledger that your customers, regulators, and partners can verify. It’s more complex to build, but it resolves the governance risk without sacrificing network effects. For enterprise decisions between private and public blockchain architecture, the hybrid model is increasingly the answer that avoids both extremes.
Model
Best For
Key Risk
2026 Adoption
Private
Internal traceability, automation
No network effect
54% enterprise share
Consortium
Multi-party supply chains
Governance collapse (TradeLens)
Growing post-2025 with neutral models
Hybrid
Regulated industries (pharma, food, finance)
Integration complexity
Emerging standard in 2026
One underreported consideration: the architecture you choose for blockchain is the architecture you’re choosing for your AI supply chain deployment. Blockchain and AI are converging in every serious 2026 implementation. Your data model, access controls, and ledger structure will determine what your AI can see, predict, and automate. Choosing the wrong blockchain architecture today creates a 5-year knock-on effect on your AI capabilities. This isn’t a separate decision. It’s the same decision.
What Can Go Wrong: Four Scenarios That Kill Blockchain Projects
92% of early blockchain projects failed, according to Supply and Demand Chain Executive (December 2024). That number isn’t a reason to avoid blockchain. It’s a reason to understand exactly which failure modes to avoid. There are four.
1. The Consortium Trap
Already covered above, but worth stating plainly: if your blockchain value proposition depends on competitors sharing data on a platform you own, you’re building TradeLens. Map the incentive structure of every participant before you design the governance model. If you can’t answer “what does the second-biggest player gain by staying in this network when they start losing deals?”, you haven’t finished your architecture.
2. The Legacy Integration Sinkhole
ERP and WMS integration represents 30 to 50% of total blockchain implementation cost. This figure is consistently underestimated in project scoping. A mid-market manufacturer with SAP, a legacy WMS, and five third-party logistics providers is looking at a middleware problem that dwarfs the blockchain implementation itself. The MDPI Applied Sciences review (May 2025) confirms this: integrating blockchain into legacy systems “requires careful API design and middleware development” that is routinely underreported in ROI projections. Budget this before you launch, not after.
3. The Oracle Problem
Blockchain is immutable and auditable. It is not magic. The system records exactly what you put into it. If a supplier scans fraudulent provenance data at the farm gate, the blockchain faithfully preserves that lie forever. The oracle problem is the gap between the physical world and the digital ledger. IoT sensors, physical audits, and verification protocols are the only way to close it. A blockchain without reliable data inputs is a highly sophisticated record of whatever someone decided to type.
4. Regulatory Whiplash: GDPR vs. Immutability
GDPR Article 17, the right to erasure, is structurally incompatible with an immutable ledger. If your supply chain includes EU personal data (supplier employee records, customer-linked shipment data), you have a legal tension that needs to be resolved at the architecture level, not the legal team level. Zero-knowledge proofs and off-chain data storage with on-chain hashes offer partial solutions, but they add significant complexity. Healthcare supply chains face the same conflict with HIPAA. Budget the compliance architecture as a first-class project requirement, not an afterthought. For teams working through smart contract security risks in enterprise deployment, these governance and compliance layers are where the real exposure sits.
The 92% failure rate in context
Most of those failed projects were underfunded pilots with poor governance design, not full enterprise deployments. The distinction matters. A $50,000 proof-of-concept that gets cancelled is a failed project. It’s not the same failure mode as a $50 million TradeLens shutdown. Know which category your project is in before you start.
“The value proposition of harnessing blockchain technology to transform supply chains is not new. But 2024 and 2025 represent the shift from experimentation to execution. Companies reaching a crossroads must decide to scale or fall behind.”
Clare Adelgren, Global Head of Blockchain Sales and Operations, EY — December 2024, Supply and Demand Chain Executive
The AI Convergence: Why 2026 Architecture Choices Are 5-Year Bets
The strongest blockchain supply chain deployments in 2025 and 2026 don’t run on blockchain alone. They layer three technologies that solve fundamentally different problems: blockchain for immutable record, IoT for real-world data feeds, and AI for predictive risk, anomaly detection, and dynamic pricing. The combination is more powerful than any single piece.
Blockchain gives AI something it desperately needs: trustworthy historical data. Every AI prediction is only as good as the training data behind it. A supply chain AI trained on blockchain-verified shipment records, temperature logs, customs clearance times, and supplier performance data is making predictions from ground truth. An AI trained on reconciled spreadsheets is making predictions from the best available guess.
Gartner’s March 2025 supply chain tech trends report identifies AI convergence as the defining differentiator for 2025 and 2026. VeChain’s $15 million StarGate program, launched in July 2025 to accelerate enterprise-grade EVM-equivalent applications, is one of the clearest signals that serious capital is flowing into exactly this convergence. AWS Outposts added blockchain support in January 2025. The infrastructure is building itself around this stack.
The implication for enterprise architects is direct: the blockchain architecture decision you make in the next 12 months is simultaneously your AI supply chain architecture decision for the next five years. Your data model, your smart contract structure, and your ledger access controls will determine what your AI can see, predict, and automate in 2028 and beyond. This isn’t a blockchain project. It’s an infrastructure bet.
FAQ: Blockchain Supply Chain Management
How does blockchain improve supply chain management?
Blockchain improves supply chain management by creating a shared, tamper-proof ledger that every participant can access in real time. It eliminates manual reconciliation, reduces document fraud, and enables smart contracts that trigger payments automatically. Walmart used blockchain to cut food traceability time from 7 days to 2.2 seconds. Trade finance processing times drop by an average of 81%.
What are real examples of blockchain in supply chain?
The most cited examples are: Walmart and IBM Food Trust (food traceability, 7 days to 2.2 seconds); Maersk TradeLens (tracked 67 million containers before 2023 shutdown); Nestlé (projected $47 million savings over 5 years); VeChain (luxury goods and pharma provenance); and Trust Your Supplier (supplier onboarding on permissioned blockchain). Sources: Computerworld; Northeastern University; Marketing Scoop.
Why did Maersk’s blockchain fail?
Maersk’s TradeLens blockchain didn’t fail technically. It tracked 67 million containers and cut documentation costs by 20%. It failed because competing carriers refused to share data on a platform Maersk co-owned. Academic research published in Frontiers in Blockchain (March 2025) classifies this as a commons governance failure. The technology worked. The industry politics didn’t.
What is the ROI of blockchain in supply chain?
Industry data shows blockchain in supply chain delivers ROI within 18 to 24 months for most enterprises. Specific benchmarks: 33% reduction in operational costs, 42% lower administrative costs via smart contracts, 81% faster trade finance processing, and 25% reduction in dispute management costs. 82% of executives report positive ROI within two years. Source: SQ Magazine, December 2025.
What percentage of companies use blockchain in supply chain?
Large enterprises captured approximately 73% of blockchain supply chain finance market share in 2024. Deloitte’s 2022 global blockchain survey found 55% of respondents had already adopted blockchain across industries. Blockchain-specific supply chain adoption remains concentrated in food, pharma, and retail, with 43.5% of companies still struggling with logistics partner data-sharing as recently as 2024.
Is blockchain the future of supply chain?
Blockchain is increasingly the present of supply chain, not just the future. The market grew from $3.27 billion in 2025 to $5.23 billion in 2026 and is projected to reach $21.29 billion by 2029. The most advanced 2026 implementations combine blockchain with AI and IoT. The risk isn’t whether blockchain matters. It’s which architecture you choose and whether your governance model survives contact with competitive reality.
What are the challenges of blockchain in supply chain?
Key challenges include scalability (high transaction volumes slow many networks), interoperability with legacy ERP and WMS systems, data privacy tension with GDPR and HIPAA, high implementation costs cited by 60% of small businesses, the oracle problem (blockchain records whatever data is fed into it, accurate or not), and consortium governance failures. Skills shortages affect 58% of supply chain professionals. Source: SQ Magazine; MDPI Applied Sciences, May 2025.
How much does blockchain supply chain implementation cost?
Enterprise blockchain supply chain implementation costs vary widely. Cloud-based Blockchain-as-a-Service from AWS, Azure, or Google Cloud significantly reduces upfront costs compared to on-premises deployments. Integration with legacy systems typically represents 30 to 50% of total project cost. ROI benchmarks suggest cost recovery within 18 to 24 months at scale. 60% of small businesses still cite high implementation costs as the primary barrier to entry.
What to Watch in the Next 18 Months
What you understand now that you probably didn’t before reading this: TradeLens was not a blockchain failure. It was a governance failure that happened to involve blockchain. Walmart’s 2.2-second traceability is not a marketing claim. It’s a verified operational result confirmed by the company’s VP of Food Safety. And the 67.4% of supply chain managers still on Excel are not behind by choice. They’re behind by inertia, and the gap between them and the 82% of executives reporting positive blockchain ROI within two years is widening every quarter.
Three things to watch between now and the end of 2027:
Regulatory mandates will make adoption non-optional. S.257 is a signal, not an endpoint. EU supply chain due diligence legislation and FDA track-and-trace requirements are creating compliance timelines that remove “wait and see” as a strategy. Companies that haven’t started will face deadlines imposed from outside.
AI-blockchain hybrid deployments will define the next performance gap. The companies combining immutable blockchain records with AI-driven anomaly detection and predictive logistics in 2026 will have a structural data advantage over competitors running either technology alone. This advantage compounds annually.
Governance models will make or break the next wave of consortium projects. The Frontiers in Blockchain research (March 2025) gives enterprise architects a rigorous framework for avoiding TradeLens. The projects that succeed in the next 18 months will be the ones that designed governance before they wrote a single line of smart contract code.
The blockchain supply chain management market hit $5.23 billion in 2026. It tracked 65,000+ smart contracts in logistics last year. It processed $24.7 billion in trade finance. The question for your organization isn’t whether this technology works. It’s whether your architecture, governance, and integration plan are ready for it.
Stay Ahead of Enterprise Tech That Actually Moves
The Neural Loop delivers the signal without the noise: verified data, named sources, and decisions that matter to enterprise leaders. No hype. No filler.
Subscribe to The Neural Loop
Why Your Blockchain Is Slow, Expensive, and Losing to a Startup: Layer 2 Scaling for the CTO Running Out of Patience
By NeuralWired Research Desk | June 11, 2026 | 9 min read
Quick Answer
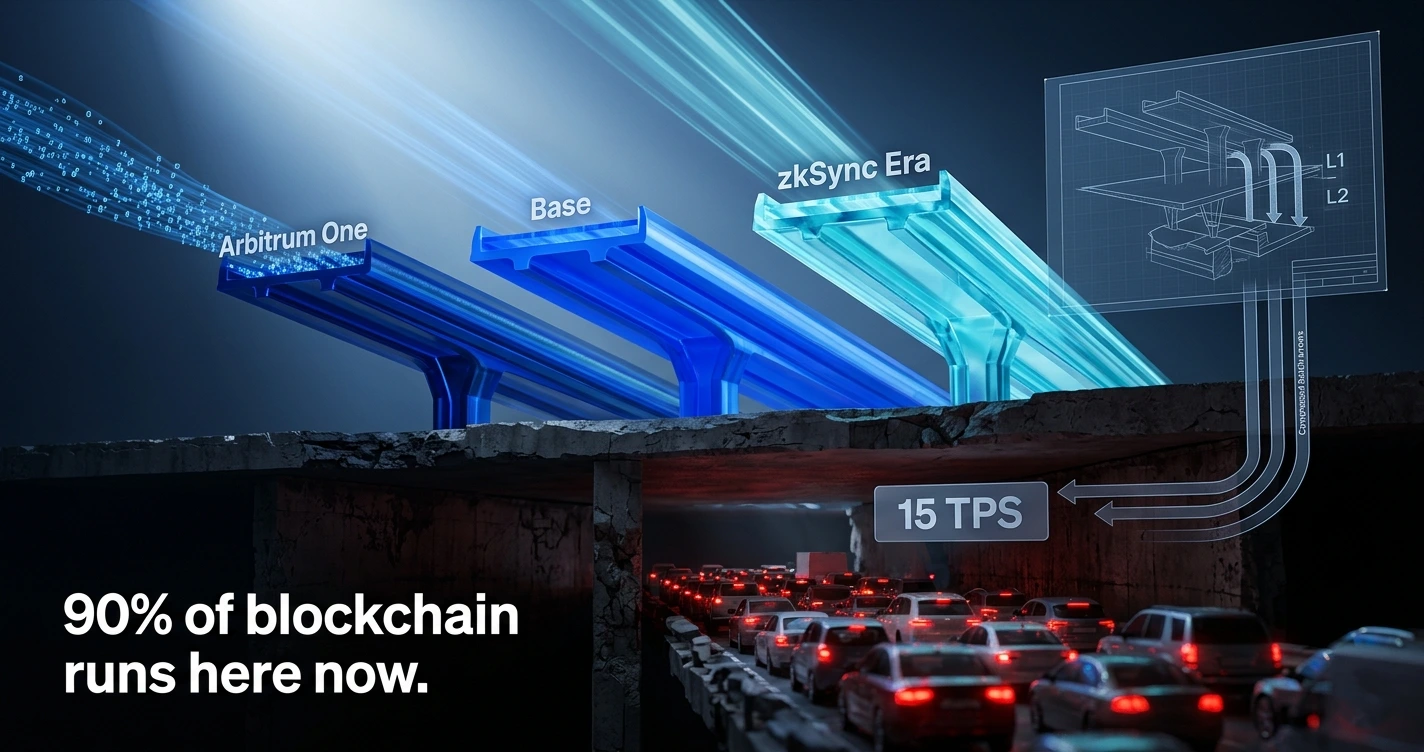
Layer 2 blockchain scaling refers to secondary protocols built on top of Ethereum or Bitcoin that process transactions off-chain, then settle the batch result to the base chain. The result: throughput jumps from 15 TPS on Ethereum L1 to 4,000–65,000 TPS, and transaction fees drop by up to 95%. As of 2026, Layer 2 handles 90% of all blockchain transaction volume. For enterprise CTOs, the strategic question is no longer whether to use Layer 2. It’s which one, and why.
Here is the situation your competitors are already in. A Web3 payments startup deploys on Arbitrum, processes 4,000 transactions per second at roughly $0.05 each, and goes live in six weeks. Your enterprise blockchain team is still on Ethereum mainnet, where the network processes 15 transactions per second during normal conditions and gas fees spike to $30–$50 per transaction under load. That is not a minor inefficiency. That is a structural cost disadvantage that compounds every day you wait.
This guide is not an introduction to blockchain. You’ve read those. This is the infrastructure decision brief your team needs before the next architecture review, written for CTOs who are done with the hype and ready for the math.
The Numbers That Should Alarm Your Board
The performance gap between Layer 1 blockchains and enterprise payment networks is not a detail. It’s the central fact of the entire Layer 2 thesis.
7
TPS — Bitcoin L1
15–30
TPS — Ethereum L1
1,700
TPS — Visa network
4,000+
TPS — Arbitrum Layer 2
65,000
TPS — Polygon peak
Visa processes roughly 1,700 transactions per second. Ethereum mainnet processes 15–30. Bitcoin processes 7. L2Beat data confirms that as of December 2025, total Ethereum L2 networks hold over $36 billion in bridged assets and collectively handle 90% of all Ethereum-related transaction volume. The shift has already happened. The question is whether your infrastructure has caught up.
Enterprise blockchain spending is projected to reach $145.9 billion by 2030, growing at a 47.4% CAGR. The teams winning that market are not building on Layer 1 for general execution. Over 65% of all new smart contract deployments in 2025 went directly onto Layer 2 networks, not Ethereum mainnet. That is the developer vote, expressed in production deployments.
Why Layer 1 Is Slow by Design
The slowness is not a bug. It’s an intentional trade-off baked into every major Layer 1 blockchain. Every blockchain faces what researchers call the trilemma: you can optimize for two of three properties simultaneously, but not all three.
Property
What It Means
L1 Choice
Security
Transactions cannot be reversed by attackers without controlling majority of network
✓ Maximized
Decentralization
No single party controls the network; thousands of independent validators
✓ Maximized
Scalability
High transaction throughput at low cost
✗ Sacrificed
Ethereum and Bitcoin chose security and decentralization. That is why every full node must process every transaction, why block times are measured in seconds rather than milliseconds, and why gas fees reflect real competition for limited block space.
Layer 2 breaks this trade-off rather than choosing within it. By executing transactions off-chain and submitting only a compressed proof or batch result to Layer 1 for final settlement, Layer 2 borrows Layer 1’s security without forcing Layer 1 to do the execution work. The base layer becomes what Ethereum’s roadmap explicitly describes: a settlement and data availability layer. Layer 2 becomes where computation actually happens.
The Four Layer 2 Mechanisms, Explained
Layer 2 is not a single technology. There are four distinct architectural approaches, each with different trade-offs that matter directly for enterprise deployment decisions.
1. State Channels
Two parties lock funds in a smart contract, transact freely off-chain at zero cost, then close the channel and settle the final state on Layer 1. The Bitcoin Lightning Network is the canonical example. Ideal for high-frequency bilateral transactions (micropayments, gaming credits). Not suitable for multi-party or complex smart contract interactions.
2. Sidechains
An independent blockchain that runs alongside Layer 1 with its own consensus rules and validator set. It connects to the main chain via a bridge but does not inherit Layer 1 security directly. Polygon PoS operates as a sidechain. Fast and cheap, but the security guarantee is only as strong as the sidechain’s own validator set, not Ethereum’s.
3. Optimistic Rollups
Transactions are executed off-chain and batched. The batch is posted to Layer 1 and assumed valid unless someone submits a fraud proof within a challenge window (typically 7 days). EVM-compatible out of the box, which means your existing Solidity contracts migrate with minimal changes. Arbitrum One, Optimism (OP Mainnet), and Base are optimistic rollups. They dominate by TVL and transaction volume today. The 7-day withdrawal delay is the core operational limitation.
4. ZK-Rollups (Zero-Knowledge Rollups)
Transactions are executed off-chain, and a cryptographic proof (a SNARK or STARK) is generated that mathematically proves the validity of the entire batch before it’s submitted to Layer 1. No challenge window. Near-instant finality. Stronger privacy potential. zkSync Era achieved full EVM bytecode equivalence in mid-2025, meaning Solidity contracts now deploy without modification. StarkNet uses its own Cairo language, which delivers superior performance but requires developer reskilling. ZK-rollups currently hold about 10% of L2 TVL, roughly $3.5 billion, but represent the direction enterprise infrastructure is heading.
Our Read
The optimistic vs. ZK choice is the most consequential architecture fork you’ll make in 2026. Optimistic rollups give you liquidity and tooling today. ZK-rollups give you faster finality and compliance-grade privacy tomorrow. For most enterprise CTOs, optimistic rollups are the safe production choice now, with a migration path to ZK when the ecosystem matures.
The L2 Landscape: Who’s Winning and Why
In 2024 and 2025, hundreds of new Layer 2 networks launched. Nearly all of them are now dormant. The Block’s 2026 Layer 2 Outlook is unambiguous: most new L2s saw usage collapse once token incentive cycles ended. Only a handful of networks have self-sustaining ecosystems. Those are the only ones worth your consideration.
Network
Type
TVL
Peak TPS
Avg. Fee
Finality
Best For
Arbitrum OneLeader by TVL
Optimistic Rollup
$16.63B (44% share)
4,000 TPS
~$0.05
7-day (L1)
DeFi, finance, high-value contracts
BaseLeader by volume
Optimistic Rollup (OP Stack)
Growing rapidly
High
~$0.01–0.05
7-day (L1)
Consumer apps, Coinbase fiat on-ramp
Optimism
Optimistic Rollup
$2–3B
High
~$0.05
7-day (L1)
DeFi, Superchain interoperability
zkSync Era
ZK-Rollup
~$1B
Very high
~$0.01
Minutes
Privacy-sensitive apps, compliance
StarkNet
ZK-Rollup (STARK)
~$1B
Very high
~$0.01
Minutes
High-security apps, Cairo-native teams
Polygon zkEVM
ZK-Rollup
Moderate
High
Low
Minutes
Enterprise EVM migration
Immutable X
ZK-Rollup (specialized)
Niche
4,000 TPS
Zero gas
Fast
NFT, gaming studios
Arbitrum One commands approximately 44% of total L2 TVL at $16.63 billion as of November 2025, per BlockEden’s analysis. For enterprise DeFi and financial application deployment, its liquidity depth makes it the default choice. Its February 2025 Stylus upgrade added WebAssembly support alongside EVM execution, meaning your Rust and C++ developers can now write smart contracts without learning Solidity. That is a meaningful change for enterprise engineering teams.
Base, built by Coinbase on the OP Stack, has emerged as the dominant network by transaction volume, handling roughly 46% of all L2 transactions and generating approximately $75.4–$82.6 million in revenue across 2025. For any enterprise application that needs to onboard users directly from traditional finance, Base’s integration with Coinbase’s 110 million-plus user base and native fiat on-ramp is an operational advantage no other L2 currently matches.
One critical development that accelerated the entire L2 cost structure: EIP-4844, deployed in 2024, introduced a new data type called “blobs” that cut L2 data costs by 10x in a single upgrade. Before EIP-4844, L2 fees were cheap-ish. After it, they became genuinely viable for enterprise use at scale. Arbitrum averages about $0.05 per transaction versus $1–$50 on Ethereum mainnet during peak periods. zkSync Era comes in at roughly $0.01.
Use Case Matrix: Which L2 for Which Enterprise Job
Enterprise Use Case
Recommended L2
Why
DeFi treasury operations and cross-border payments
Zero gas fees, 4,000 TPS, purpose-built for digital assets
Supply chain settlement with smart contract complexity
Arbitrum One or Polygon zkEVM
EVM compatibility, developer tooling, audit trail on L1
High-frequency micropayments between known parties
Lightning Network (Bitcoin)
Zero marginal cost per transaction, bilateral settlement
The documented ROI case for ZK-proof applications is worth pausing on. A 2025 enterprise deployment using ZK proofs on Layer 2 cut KYC refresh cycles from 10 days down to 3 hours, while avoiding $18 million in regulatory fines through automated compliance reporting. Those are not hypothetical projections. They’re the kind of numbers a CFO understands immediately.
The Real Risks Nobody Is Talking About
Layer 2 is the right direction. That doesn’t mean you can ignore the specific failure modes. Three of them are severe enough to have cost the industry over $900 million in a single year.
Bridge Vulnerabilities Are the Highest-Risk Surface in the Stack
The Ronin bridge hack in March 2022 cost $600 million. The Wormhole hack in February 2022 cost $321 million. Both occurred because bridge smart contracts, the on-ramps and off-ramps between Layer 1 and Layer 2, were either misconfigured or insufficiently audited. Bridges are where your enterprise deployment is most exposed. Before any cross-L2 operation, a formal smart contract audit is not optional. See our Smart Contract Audit Checklist 2026 and our companion audit guide for enterprises before any L2 deployment.
Operational Risk Alert
A mid-size enterprise deploys a token on Arbitrum. A partner needs liquidity on zkSync. Moving funds across requires bridging. Optimistic rollup withdrawal delays mean $2 million in working capital could be inaccessible for 7 days. That is not a hypothetical scenario. It’s a documented class of operational failure that enterprise treasury teams regularly encounter.
Sequencer Centralization Is an Audit and Compliance Risk
In 2026, roughly 45% of Layer 2 ecosystems face sequencer centralization concerns, according to CoinLaw’s research compilation. Most major optimistic rollups still operate with a single, centralized sequencer that determines transaction ordering. That is a single point of failure. Sequencer downtime means transaction failure. Sequencer censorship (Sony’s Soneium attempted exactly this via its L2) means your transactions can be selectively blocked.
Vitalik Buterin himself confirmed in February 2026 that most L2s remain at Stage 0 or Stage 1 decentralization, where centralized Security Councils retain the ability to revert transactions. For an enterprise CTO building compliance-grade financial infrastructure, deploying on a chain whose operators can reverse transactions is not a blockchain. It’s a managed database with extra steps and extra cost.
Liquidity Fragmentation Is Getting Worse, Not Better
CoinShares analyst Max Shannon documented this in institutional research that remains the most-cited critique of L2 proliferation heading into 2026.
“With their asynchronous sequencing and zero-sum proprietary technology stacks, L2 solutions exacerbate fragmentation, posing significant challenges to liquidity, interoperability, and social coordination.”
Max Shannon, Analyst, CoinShares Research — via The Block, August 2024
The data behind that assessment is concrete. Average liquidity depth across L2 networks has declined by 40%. Sixty-two percent of users report difficulty managing bridging and wallets across multiple L2s. An enterprise deploying across several L2s faces real coordination overhead that shows up as treasury cost and developer time, not just theoretical complexity.
The Ghost Town Problem
The Block’s December 2025 analysis confirmed what on-chain data already showed: most new L2s that launched in 2024–2025 are now functionally dead. Their usage collapsed the moment token incentive programs ended. If your enterprise infrastructure team is evaluating a newer or smaller L2 to capture lower fees, the operational risk is deployment on an ecosystem that gets abandoned six months after you go live. Stick to the top five networks by TVL, verified on L2Beat, as your shortlist.
The Counter-Argument: Is Layer 2 Even the Right Answer?
The Layer 2 narrative is the mainstream position in 2026. But two credible voices are challenging it from different angles, and a serious CTO should understand both before committing architecture.
The Case for Integrated Layer 1 (Sompolinsky / Kaspa)
“Ethereum suffers a lot from modularity. Solana succeeded because they did not have this. Everything goes on the same Layer 1.”
Yonatan Sompolinsky, Founder of Kaspa and co-author of the GHOST protocol — TheStreet Crypto, February 26, 2026
Sompolinsky’s argument is not theoretical posturing. Solana processes approximately 65,000 TPS on a single, coherent state layer. No bridges. No withdrawal delays. No sequencer risks. No liquidity fragmentation. For enterprises that don’t specifically need Ethereum’s DeFi liquidity, a high-throughput integrated Layer 1 may genuinely outperform a modular L2 stack when total operational complexity is priced in.
Vitalik Buterin’s Warning About His Own Ecosystem
In February 2026, Ethereum co-founder Vitalik Buterin issued two pointed warnings. First, that progress toward Stage 2 decentralization across L2s is “far slower than expected” and that most chains remain under centralized control. Second, that generic EVM-compatible L2s with no differentiation represent “a failure of imagination” and are no longer viable as a product strategy.
Our read: this signals a consolidation phase. The Arbitrums, Bases, and zkSyncs of the world will absorb the market share of undifferentiated competitors. For enterprise CTOs, this accelerates the “stick to top-5-by-TVL” rule rather than undermining the L2 thesis overall. But it does validate the concern that the L2 ecosystem is not yet the stable, decentralized infrastructure layer it was projected to be by 2025.
For a broader view of why the world’s largest bank moved away from private blockchain entirely, our analysis of JPMorgan’s public blockchain pivot is directly relevant context here. The TradeLens shutdown (IBM and Maersk’s private blockchain consortium, which handled over 50% of global ocean container cargo data before shutting down in 2022 after five years and 300 members) demonstrated that private consortium architectures hit a structural ceiling when they require universal industry participation. Layer 2 on public infrastructure solves a different problem than private chains ever could.
Frequently Asked Questions
What is Layer 2 blockchain scaling?
Layer 2 blockchain scaling refers to secondary protocols built on top of a base blockchain (Layer 1) that process transactions off-chain and settle the results back to the main chain. This increases throughput from 15 TPS on Ethereum L1 to 4,000–65,000 TPS while reducing transaction fees by up to 95%. As of 2026, Layer 2 networks collectively process 90% of all blockchain transactions by volume.
What is the difference between Layer 1 and Layer 2 blockchain?
Layer 1 is the base blockchain (Ethereum, Bitcoin) handling security and consensus. Layer 2 runs on top of it to process transactions faster and cheaper. Layer 1 handles final settlement; Layer 2 handles execution. As of 2026, Layer 2 processes 90% of blockchain transactions while Layer 1 provides the security anchor.
Is Layer 2 blockchain secure?
Layer 2 inherits Layer 1 security for settled transactions, but introduces specific new risks: bridge vulnerabilities (the Ronin hack lost $600M via a bridge exploit), centralized sequencers that can fail or censor, and smart contract bugs. Security varies by L2 type. ZK-rollups are cryptographically more rigorous than optimistic rollups because validity is proven upfront, not assumed and challenged later.
Which Layer 2 blockchain is best for enterprise?
It depends on the use case. Arbitrum (44% of L2 TVL at $16.63B) is the default for DeFi and financial applications. Base is best for consumer apps requiring Coinbase fiat on-ramps. zkSync Era and StarkNet are best for privacy-sensitive applications needing fast finality. Always verify the network’s security stage rating on L2Beat before committing to a deployment.
What is a ZK-rollup and how does it work?
A ZK-rollup batches transactions off-chain and generates a cryptographic proof (a SNARK or STARK) that mathematically verifies the validity of the entire batch before submitting the result to Layer 1. This enables near-instant finality and stronger privacy properties than optimistic rollups. zkSync Era and StarkNet are the leading ZK-rollup platforms as of 2026.
What is an optimistic rollup?
An optimistic rollup processes transactions off-chain, assuming they’re valid unless someone submits a fraud proof within a 7-day challenge window. They are EVM-compatible out of the box, making Solidity migration straightforward. Arbitrum, Optimism, and Base are the leading optimistic rollup platforms and dominate Layer 2 by total value locked and transaction volume.
Why is Ethereum so slow and expensive?
Ethereum Layer 1 processes approximately 15–30 TPS because its decentralized consensus requires every full node to process every transaction, prioritizing security and decentralization over speed. During high-demand periods, users compete for limited block space, driving gas fees sharply higher. Layer 2 solutions solve this by processing transactions off-chain and batch-settling on Ethereum mainnet.
What is TVL in Layer 2?
TVL (Total Value Locked) in Layer 2 represents the total value of crypto assets deposited into L2 bridge contracts from Ethereum mainnet. It’s the primary metric for measuring an L2’s adoption and liquidity depth. As of December 2025, total Ethereum L2 TVL surpassed $36 billion, with Arbitrum One holding the largest share at approximately $16.63 billion, per L2Beat.
What are the risks of Layer 2 blockchain?
Key Layer 2 risks include bridge hacks (over $900M lost in Ronin and Wormhole exploits alone), centralized sequencer failure or censorship, liquidity fragmentation (average L2 liquidity depth down 40%), 7-day withdrawal delays for optimistic rollups, and regulatory uncertainty affecting 53% of L2 DeFi projects. Sequencer centralization is a concern in roughly 45% of L2 ecosystems.
How much does a Layer 2 transaction cost?
Costs vary by network. Arbitrum averages roughly $0.05 per transaction versus $1–$50 on Ethereum mainnet during peak demand. zkSync Era averages around $0.01. Optimism reduces costs by approximately 90% versus mainnet. The 2024 EIP-4844 upgrade (proto-danksharding) cut L2 data costs by roughly 10x, making current fee levels possible at scale.
Before your team commits to any Layer 2 deployment, work through this checklist. Each point maps directly to a documented failure mode or competitive decision your architecture review needs to address.
Benchmark your current L1 transaction costs against Arbitrum and Base equivalents. The delta is measurable within a week. If you’re paying more than $0.50 per transaction on Ethereum mainnet for any high-frequency operation, the cost case for L2 migration closes immediately.
Check the network’s security stage on L2Beat before any commitment. Stage 0 means a centralized Security Council can revert your transactions. Stage 2 means trustless operation with no privileged operators. Most L2s in 2026 are still at Stage 0 or Stage 1. Know exactly what you’re accepting.
Audit the sequencer architecture. Ask: who controls transaction ordering? What happens if the sequencer goes offline? What is the SLA for sequencer uptime, and who is contractually accountable for it? Enterprise financial infrastructure requires answers before deployment.
Decide your finality requirement before choosing rollup type. If your use case can tolerate a 7-day window for full Layer 1 finality (most enterprise DeFi can), optimistic rollups give you deeper liquidity today. If you need minutes-to-hours finality for compliance or counterparty settlement, ZK-rollups are the correct choice regardless of current ecosystem size.
Verify the network is in the top 5 by TVL on DeFiLlama or L2Beat. The ghost-town problem is real. Usage collapse after incentive cycles is not a risk; it’s a documented pattern across hundreds of L2s launched in 2024–2025. Only deploy on networks with self-sustaining ecosystems.
Commission a formal smart contract audit before going live on any L2 bridge. The Ronin and Wormhole exploits were not zero-day vulnerabilities. They were known risk surfaces that weren’t adequately audited. Review our Smart Contract Audit Checklist 2026 for the complete pre-deployment framework.
What Enterprise CTOs Understand Now That They Didn’t in 2024
The strategic frame has shifted. In 2024, the question was whether to use blockchain at all. In 2026, that question is settled: 90% of blockchain transaction volume runs on Layer 2, $36 billion in enterprise and institutional capital is locked across L2 networks, and over 65% of new smart contract deployments go directly to Layer 2, bypassing Ethereum mainnet entirely.
The question your architecture team needs to answer in the next 90 days is which L2 fits your specific use case, and what your migration plan looks like if you’re still on Layer 1 for general execution. The cost penalty for delay is not theoretical. It compounds every transaction cycle.
Over the next 12 to 18 months, watch for three developments that will reshape the L2 decision matrix. First, progress (or continued lack of progress) toward Stage 2 decentralization across the major optimistic rollups. Vitalik’s February 2026 warnings were a direct challenge to every major L2 team. Second, ZK-rollup ecosystem maturity. If zkSync Era and StarkNet close the developer tooling gap with Arbitrum, the case for ZK-first enterprise deployment strengthens significantly. Third, cross-chain interoperability infrastructure. LayerZero and native bridge improvements are attempting to solve the liquidity fragmentation problem directly. Their success or failure will determine whether the L2 ecosystem consolidates or fragments further.
For enterprises still evaluating whether public Layer 2 or a private consortium approach is the right foundation, the JPMorgan case study in our public vs. private blockchain analysis is the clearest real-world benchmark available. And for any team moving into L2 smart contract deployment, the 2026 audit checklist is the pre-flight check your security team needs before the first transaction goes live.
Layer 2 is not a future state. It’s the current operating environment for enterprise blockchain. The infrastructure is built. The liquidity is deployed. The developer tooling is production-ready. What’s left is your migration timeline.
Stay Ahead of Enterprise Blockchain Infrastructure
The Neural Loop delivers NeuralWired’s weekly analysis on blockchain, AI, and enterprise technology to 40,000+ CTOs and engineers. No noise. No hype. Just the decisions that matter.
Subscribe to The Neural Loop