Designing and constructing roads with safety and protection in mind is a crucial aspect of urban planning. Roads are essential elements of any metropolitan area, and incorporating safety features can significantly enhance the well-being of both pedestrians and motorists. Here are several considerations for building roads with protection in mind:
Pedestrian Infrastructure:
Sidewalks:
Ensure well-maintained and spacious sidewalks separated from the road to provide a safe walking environment.
Crosswalks:
Implement marked crosswalks at intersections to guide pedestrians safely across the road. Pedestrian Overpasses/Underpasses: Consider constructing overpasses or underpasses in areas with high pedestrian traffic to minimize the risk of accidents.
Cyclist-Friendly Design:
Bike Lanes: Incorporate dedicated bike lanes separated from vehicular traffic to promote cycling safety. Bike Racks: Install bike racks at strategic locations to encourage cycling and provide secure places for parking.
Traffic Calming Measures:
Speed Bumps: Use speed bumps in residential areas and near schools to reduce vehicle speeds. Roundabouts: Implement roundabouts instead of traditional intersections to slow down traffic and improve safety.
Accessible Infrastructure:
ADA Compliance:
Ensure that road infrastructure is compliant with the Americans with Disabilities Act (ADA) to accommodate individuals with disabilities. Accessible Crossings: Install ramps and accessible crossings to facilitate the movement of people with mobility challenges.
Road Lighting:
Streetlights:
Adequate street lighting enhances visibility, reducing the risk of accidents and improving overall safety. Pedestrian Crosswalk Lighting: Install additional lighting at crosswalks to increase visibility for both pedestrians and drivers. Green Spaces and Landscaping:
Roadside Greenery:
Incorporate green spaces and landscaping along roads, providing aesthetic value while also promoting a sense of safety.
Tree Planting:
Plant trees strategically to provide shade and improve air quality. Advanced Traffic Management Systems:
Traffic Signals:
Implement modern traffic signal systems to optimize traffic flow and enhance safety.
Smart Crosswalks:
Use technologies such as smart crosswalks that provide signals or warnings to both pedestrians and drivers.
Emergency Services Access:
Emergency Lanes:
Designate lanes or routes for emergency vehicles to ensure quick and unobstructed access during emergencies.
Public Awareness and Education:
Signage:
Install clear and visible signage to communicate speed limits, pedestrian crossings, and other important information.
Educational Campaigns:
Conduct public awareness campaigns to educate residents about road safety and proper usage of infrastructure. By incorporating these elements into road design, metropolitan areas can create safer and more sustainable environments for their residents. Collaborative efforts between urban planners, engineers, and the community are essential to ensuring that road infrastructure prioritizes protection and safety.
US vs EU vs China AI Regulation 2026: Which Approach Is Actually Winning?Policies
The US Said Move Fast. The EU Said Prove It’s Safe. China Said Nothing and Filed 38,000 AI Patents. Which AI Regulation Is Actually Winning in 2026?
By NeuralWired Research Desk | June 24, 2026 | 14 min read
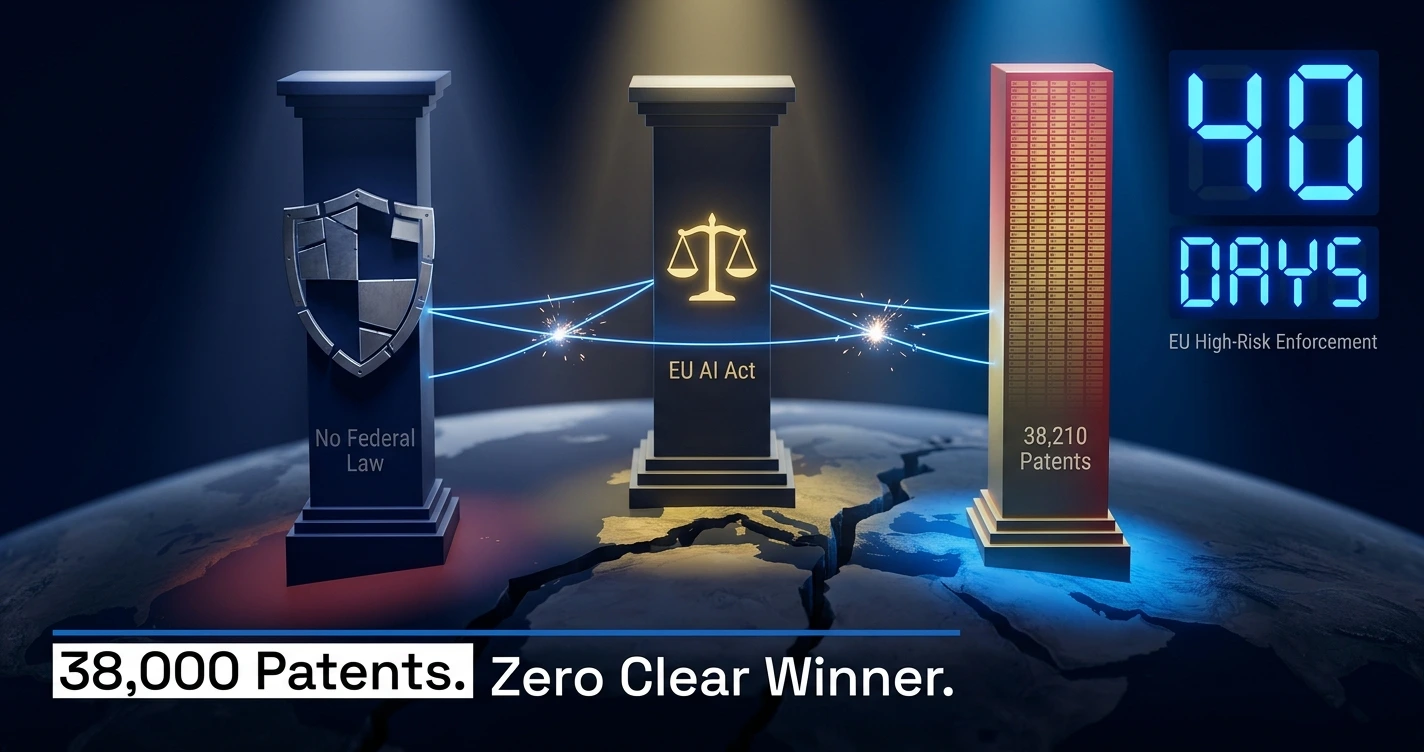
On August 2, 2026, forty days from today, the EU begins enforcing high-risk AI regulation rules against every company on earth that touches a European user. The fines cap at €35 million or 7% of global revenue, whichever is higher. Only 18% of organizations have a fully implemented AI governance framework. Do the math.
Meanwhile, the United States has spent 2025 and 2026 systematically dismantling the modest federal guardrails that existed, threatening to cut broadband funding to any state that dares write its own AI law, and watching its frontier model lead over China shrink from 9.26 percentage points in January 2024 to 2.7 percentage points by March 2026. And China? China filed 38,210 generative AI patents between 2014 and 2023. The US filed 6,276.
This is the AI regulation comparison that actually matters in 2026. Not who wrote the most thoughtful white paper, but who is winning on the metrics that determine whether AI becomes a strategic asset or a liability over the next decade. The answer is more unsettling than any of the three governments will admit.
The Race That Isn’t a Race
Before scoring the contestants, it’s worth questioning the framing itself. Prof. Rostam Neuwirth, a law professor at the University of Macau who researches AI regulatory comparative law, puts the problem directly:
“This terminology also has a temporal aspect, which means that different jurisdictions are competing or ‘racing’ to adopt laws regulating AI which, however, is not only detrimental to finding the optimal moment for regulatory intervention, but likely also obstructs the establishment of a future-proof regulatory framework for a rapidly evolving technology.”
Prof. Rostam Neuwirth, University of Macau, Communications of the ACM, February 2026
Neuwirth’s deeper concern is harder to ignore: “The single biggest unaddressed risk is not a technical failure, but a human one: the failure to renew the debate on humanity’s long-range goals in an age of transformative technology.”
That said, the race framing exists because it describes something real. The US, EU, and China are making fundamentally different bets on the same question: does governing AI before you know what it can do make you safer, or just slower? The three answers on offer are move fast, prove it, and don’t ask. Each carries a specific set of risks that are now materializing.
The United States: Move Fast, Remove Guardrails
The Deregulatory Playbook
On January 23, 2025, President Trump signed Executive Order 14179, revoking Biden’s AI safety order (EO 14110) on day one of his second term. The core policy: “sustain and enhance America’s global AI dominance” through a “minimally burdensome” regulatory framework. The directive told OMB to revise its AI memoranda within 60 days and mandated an AI Action Plan within 180 days.
That action plan arrived July 23, 2025, anchored to three pillars: accelerating innovation, building AI infrastructure, and leading in international AI diplomacy. The framing was “Build Baby Build.” Three more executive orders accompanied it, covering federal AI procurement and infrastructure.
Then, in December 2025, the administration went further. A new executive order explicitly targeted state-level AI regulation as a threat to innovation, mobilizing the DOJ to challenge “onerous” state AI laws through litigation and conditioning broadband funding through the BEAD Program on states not enacting conflicting AI laws. Colorado’s algorithmic discrimination law was called out by name. An attempted 10-year moratorium on state AI laws, bundled into the “One Big Beautiful Bill Act,” was defeated in the Senate in January 2026. The war on state regulation continues through other means.
What the US Actually Has
Here’s what the US regulatory architecture looks like on the ground as of June 2026: no comprehensive federal AI law, a patchwork of sector-specific oversight through the FTC, FDA, EEOC, and CFPB, 1,000-plus AI-related bills introduced across states and territories in 2025 alone, and California SB 942 (AI transparency requirements) in force since January 1, 2026.
The “no regulation” narrative is misleading, though. US federal agencies issued 59 AI-related regulations in 2024, more than double the 2023 count, from twice as many agencies, according to the Stanford HAI AI Index 2025. The US does regulate AI. It just does so in silos, without any unified framework, and without anyone clearly in charge when something crosses sector lines.
Political Risk
Only 31% of Americans trust their own government to regulate AI effectively, the lowest level of any surveyed country globally, according to the Stanford HAI 2026 AI Index. The administration is removing safeguards that its own public doesn’t believe it can manage responsibly. That’s a political time bomb if a high-profile AI harm event lands during an election cycle.
The US also declined to sign the Paris AI Action Summit’s “Statement on Inclusive and Sustainable AI” in February 2025, alongside the UK. China signed it. That absence from the multilateral table is a choice with strategic consequences that haven’t fully played out yet.
The Private Capital Argument
The strongest argument for the US approach is the investment gap. Stanford HAI’s 2026 AI Index puts US private AI investment at $285.9 billion in 2025, 23.1 times greater than China’s $12.4 billion and 63 times greater than the UK’s. Global corporate AI investments hit $581.7 billion in 2025, up 130% from 2024. The US is capturing a disproportionate share of that capital precisely because it has kept barriers low.
The counterargument matters, though. Chinese government guidance funds are estimated to have deployed $184 billion from 2000 to 2023, with broader estimates reaching $912 billion across all industries including AI. The headline 23x private capital advantage collapses when state funding is incorporated into the calculation.
The European Union: Prove It’s Safe or Pay the Price
The Law That Changed the Rules
Regulation (EU) 2024/1689, the EU AI Act, is the world’s first comprehensive, legally binding AI framework. It entered into force August 1, 2024, and has been in phased rollout since. The structure is a risk-tiered pyramid: prohibited practices at the top (already enforceable since February 2025), General Purpose AI model obligations in the middle (active August 2025), and high-risk system compliance at the foundation (August 2, 2026).
The penalty structure exceeds GDPR. Prohibited AI violations carry fines up to €35 million or 7% of global annual turnover. High-risk violations: €15 million or 3%. Even incorrect information submitted to regulators: €7.5 million or 1%. GDPR tops out at €20 million or 4% of turnover. The EU has deliberately designed the AI Act to cost more than ignoring it.
What’s Enforced Right Now
The EU AI Office is not waiting for August. In January 2026, it issued a formal order for X (formerly Twitter) to retain all internal data related to its AI chatbot Grok. It launched an investigation into Meta’s WhatsApp Business APIs. Multiple investigations into workplace emotion recognition and social scoring systems are underway. No public fines have been issued as of June 2026, but the enforcement apparatus is visibly active.
On the GPAI (General Purpose AI) side, 26 major providers signed the Code of Practice when it became active in August 2025. Microsoft, Google, Amazon, OpenAI, and Anthropic are all signed. Meta refused. That refusal triggered “Ecosystem Investigations” and exposure to 7% global revenue penalties. Meta’s confrontational approach is, as of this writing, the clearest case study in what not to do under the EU AI Act framework.
The May 2026 Delay and What It Means
On May 7, 2026, EU lawmakers reached political agreement through the Digital Omnibus package to delay several high-risk AI compliance deadlines. Standalone Annex III high-risk systems get a 16-month postponement to approximately December 2027. Products covered by EU product safety rules get a 12-month extension. Transparency obligations for AI-generated content were pushed to December 2, 2026, only a three-month extension.
This delay has not been formally adopted as of June 24, 2026. Legal advisors across Travers Smith, McKenna Consultants, and Holland & Knight are unanimous: treat August 2, 2026 as the binding date. Any extension is schedule relief for those already substantially compliant, not a reason to delay compliance work that takes six to twelve months to complete.
40-Day Clock
If your organization deploys AI in any Annex III category, specifically hiring algorithms, credit scoring, biometrics, law enforcement tools, education assessment systems, or medical diagnostics, conformity assessments typically require six to twelve months. If you haven’t started, you are already in potential violation territory as of August 2.
40% of enterprise AI systems currently have unclear risk classifications, per a 2026 appliedAI study of 106 enterprise deployments. Get your Annex III classification done before the enforcement window opens.
The Brussels Effect: Real or Overstated?
The Brussels Effect, a concept documented by Columbia Law professor Anu Bradford, describes how EU regulations become de facto global standards because it’s more efficient for multinationals to comply with the strictest framework everywhere than to maintain regional compliance versions. The GDPR is the textbook example: €7.1 billion in cumulative fines have been issued globally, and every major tech company has restructured its data handling to EU standards rather than building separate EU-only processes.
The AI Act is already showing early Brussels Effect dynamics. Adobe and OpenAI have globally embedded C2PA (Coalition for Content Provenance and Authenticity) watermarking standards rather than building EU-only compliance modules. The EU required it; the rest of the world got it anyway.
The skeptical case is worth hearing, though. The EU produced just three notable AI models in 2024, while writing the world’s most comprehensive AI law. If the regulating entity isn’t a meaningful producer, the Brussels Effect has limited commercial payoff for Europe itself. The EU is setting rules for an industry it’s watching largely from the outside.
China: Deploy Hard, Control Tight
Not One Law but a Stack
Western coverage of Chinese AI regulation usually frames it as either “strict censorship” or “anything goes for national champions.” Both are wrong. China has actually built the most granular AI regulatory architecture of the three jurisdictions, layer by layer, without a single omnibus law until now.
The sequence: Algorithm Recommendation Measures in March 2022 (first in the world for recommender systems), Deep Synthesis Measures in January 2023 (covering AI-generated video, audio, and images, predating similar EU and US requirements), Generative AI Interim Measures in August 2023 (the world’s first binding regulation specifically for generative AI, requiring model registration, pre-launch security assessments, and legally sourced training data), and Cybersecurity Law amendments taking effect January 1, 2026, with immediate severe fines for data leaks. China’s June 2026 announcement of a unified national AI law consolidates this stack into a single framework.
The enforcement mechanism is sharply different from the EU. China can suspend services, require algorithm modifications, and demand government audits. Non-compliance doesn’t just cost money. It can mean loss of operating license. For a business, that’s existential, not just financial.
The Patent Strategy
The 38,210 versus 6,276 generative AI patent figure from the WIPO Patent Landscape Report on Generative AI is the most alarming data point in this article’s headline. China filed more than six times as many GenAI patents as the US between 2014 and 2023. In 2024, China filed 1.8 million total patent applications, accounting for 49.1% of the global total, up from 34.6% in 2014. By IP intensity relative to GDP, China files 4,977 resident applications per $100 billion of GDP, outpacing Japan (4,150) and Germany (1,241).
The quality caveat matters, though. China’s GenAI patent grant ratio is approximately 32% (Baidu is highest at 45%; others range from 22% to 30%). Most Chinese patents lack international PCT protection, meaning their legal enforceability outside China is limited. For investors and IP strategists: the question is not how many patents but how many defensible, internationally filed, commercially deployed patents. On that narrower measure, the gap narrows considerably.
The Compute Constraint
Here’s where the China-winning narrative hits its hardest structural limit. US total AI compute stands at 39.7 million petaflops, roughly 50% of global total. China’s total is 400,000 petaflops, seventh globally, below even India’s 1.2 million petaflops.
As Sean Kenji Starrs, a lecturer in International Development at King’s College London who studies global technology competition, notes: “China’s compute is the world’s seventh largest with 400,000 petaflops, far below even India’s 1.2 million petaflops. This is the result of the US export ban on Nvidia and AMD’s most advanced chips.”
That 99-to-1 compute gap is the most consequential single data point in the entire AI race discussion. It’s also the direct product of US regulatory action, not market forces. Export controls are doing strategic work that no domestic AI law has managed to replicate.
The Deployment Play Others Are Missing
The researcher cited in the Communications of the ACM analysis makes the case for China’s actual strategy clearly: “The true objective is not to restrict innovation but to coordinate and accelerate it, ensuring that its technology firms sprint forward while remaining securely under political control.”
The deployment story also extends beyond US and EU markets. China is deploying affordable AI models at scale across Global South markets where US and EU products don’t reach, are too expensive, or are politically unwelcome. Foreign Policy reported in May 2026 that frontier US models are priced beyond the reach of most of the world. China’s regulatory framework is strict on content control but permissive on commercial deployment precisely where it matters for market expansion.
The 2026 Scorecard: Who’s Actually Ahead
$285.9B
US private AI investment, 2025 (Stanford HAI)
2.7%
US lead over China’s top model (March 2026, down from 9.26%)
6x
China’s GenAI patent volume advantage over the US (WIPO 2024)
40 days
Until EU AI Act high-risk enforcement (August 2, 2026)
Metric
United States
European Union
China
Private AI Investment (2025)
$285.9 billion
~$23 billion est.
$12.4 billion (+$184B+ gov. funds est.)
Notable AI Models (2024)
40
3
15
GenAI Patents (2014-2023)
6,276
Low
38,210
AI Compute (Petaflops)
39.7 million (50% global)
Distributed across members
400,000 (7th globally)
Top Model Quality Gap (vs US)
Benchmark leader
No frontier model
2.7% behind (Mar 2026)
Regulatory Framework
Sector-specific, no federal law
Comprehensive, risk-based, binding
Layered sectoral stack, unified law incoming
Max Penalty
Varies by sector/agency
€35M or 7% global revenue
License revocation (existential)
Global Public Trust to Regulate AI
31% (lowest globally)
Higher than US or China
Unverified comparable
There is no single winner. But there is a clear asymmetry across three distinct dimensions.
The US is winning the innovation race. Private capital, frontier model production, and compute infrastructure all point the same direction. But there is no governance architecture for when something goes catastrophically wrong, and the public doesn’t trust the government to manage it. That’s a structural bet that no catastrophic failure occurs before enough political will develops to legislate properly.
The EU is winning the standards race. The Brussels Effect is real, and C2PA watermarking going global is early evidence it’s working in AI. But the EU is losing the production race badly. Three notable AI models from a market of 450 million people and the world’s most comprehensive AI law is a poor return on regulatory investment.
China is winning the deployment race. Patent volume, industrial robot installation (295,000 in 2024 versus Japan’s 44,500 and the US’s 34,200), benchmark convergence, and affordable model exports to Global South markets all point the same direction. But compute constraints and political content controls create a ceiling on global model trustworthiness that private capital alone won’t easily remove.
Starrs, who is skeptical of doomsday narratives, offers useful grounding: “We should first make clear how far ahead the US is. As of early November 2025, it boasts all of the world’s top ten AI firms by market value as well as 37 of the top 50.” The US structural advantage in commercial AI is still the dominant fact. But it is also a fact that’s getting less dominant every quarter.
Jensen Huang of Nvidia said in November 2025, “China is going to win the AI race,” then walked it back to “China is nanoseconds behind America in AI.” His incentive (relaxed export controls so Nvidia can sell more chips to China) is worth keeping in mind. Researchers at King’s College London and Queen Mary noted that “Huang should take solace in the fact that he helms the most valuable company in history, and not peddle in self-interested alarmism.” Both the original alarm and the correction are useful data points about how politicized this conversation has become.
The CTO Playbook: What This Means for Your Stack
If You Deploy Annex III AI Systems
August 2, 2026 is forty days away. If your organization deploys hiring algorithms, credit scoring models, biometric identification systems, law enforcement AI tools, education assessment systems, or medical diagnostic AI, and any of those outputs touch EU users, you are in scope for full enforcement. The conformity assessment process, including documentation, technical standards compliance, and ongoing monitoring obligations, takes six to twelve months to complete properly. The clock has functionally run out for late starters.
Even if the Digital Omnibus delay is formally adopted, treat August 2 as binding. Extensions are not relief; they’re margin for those already compliant. An organization that hasn’t started conformity work and is banking on the delay is misreading the enforcement posture of the EU AI Office.
The “Comply Up” Strategy
The dominant enterprise approach as of 2026 is to build to EU standards globally, then layer on jurisdiction-specific requirements. This works because EU requirements are the most comprehensive and well-documented. Build the audit trails, conformity assessments, and monitoring architecture for Brussels, and you have a solid foundation for US and UK requirements.
China is the critical exception. Chinese compliance is not EU compliance plus a translation layer. Algorithm registration with the Cyberspace Administration of China (CAC), content labeling requirements, mandatory security self-assessments, and the “true and accurate” output requirement have no EU equivalents. Budget for a distinct compliance track. Companies that try to extend their EU compliance program to cover China without a separate workstream are creating regulatory risk in both directions.
For Founders and AI Startups
The US deregulatory environment is genuinely advantageous for iteration speed, but it doesn’t insulate you from risk. California SB 942 took effect January 1, 2026. Colorado’s algorithmic discrimination law is active as of June 2026. If you serve any EU users, you are in scope regardless of where you’re incorporated. The assumption that federal deregulation protects you from all regulatory exposure is a compliance posture that will eventually catch up with you.
The opportunity is real. For detailed context on how US federal versus state AI law creates your current compliance environment, our US AI Regulation 2026 guide breaks down the current patchwork by sector and jurisdiction.
On the positive side, the EU’s SME provisions have been extended to small mid-cap companies. Reduced documentation requirements and lower penalty thresholds create real compliance advantages for smaller organizations. And the AI governance platform market is projected to reach $492 million in 2026 spending alone. That’s early innings for a compliance tools category that barely existed eighteen months ago.
For Investors
The 38,210 patent figure sounds alarming but requires context before it drives any investment thesis. China’s GenAI patent grant ratio is 32% to 45% depending on the filer. Most of those patents are domestically filed with limited international PCT protection. The due diligence question is not “how many patents” but “how many defensible, internationally filed, commercially deployed patents with clear freedom-to-operate in target markets.”
The compute gap is where your attention should go. China’s 400,000 petaflops versus the US’s 39.7 million petaflops represents a 99-to-1 disadvantage that is the direct product of US chip export controls on Nvidia and AMD. The $295 billion Chinese data center buildout announced in June 2026, designed to run on domestic chips and largely exclude Nvidia and AMD, is the most strategically significant recent development in the AI regulation space. If China achieves compute parity by 2028 to 2029 using domestic hardware, the patent volume plus benchmark convergence plus deployment scale equation changes substantially. Watch the Huawei Ascend chip roadmap as your leading indicator.
These aren’t catastrophism. They’re the scenarios that legal scholars, policy analysts, and the ACM’s own research are already flagging as plausible within the next 24 months. The AI regulation comparison becomes moot if any of these materialize before any jurisdiction has a functional incident response protocol.
Scenario A: The Accountability Vacuum
A foundation model trained by a US company, fine-tuned by an EU company, deployed through a Chinese distribution partner, and causing documented harm to users in all three jurisdictions triggers simultaneous regulatory investigations. Each jurisdiction points to the others’ framework as primary. No international AI incident response protocol exists. The researcher cited in the ACM analysis identified this risk directly: “The first catastrophic incident involving a frontier AI model will therefore likely occur outside the territorial jurisdiction where it was trained. In the aftermath, every legal regime will be left pointing fingers, with no single entity clearly liable.”
This isn’t hypothetical. The cross-border compliance problem is already visible in daily practice. As the same researcher notes: “An AI module deemed ‘limited-risk’ in the US could be reclassified as ‘high-risk’ under the EU’s AI Act or even be prohibited for use on certain populations in China, making cross-border contract indemnities nearly impossible to draft.”
The EU AI Office issues major fines against a US AI lab for GPAI violations post-August 2026. The Trump administration’s DOJ responds by framing it as a trade dispute and threatening tariffs. The “Brussels Effect” runs in reverse: US labs withdraw EU access or geo-block services rather than comply. The AI market fragments into incompatible regional markets. The companies most exposed in this scenario are the ones that built compliance architecture assuming a unified global framework would eventually converge. It might not.
Scenario C: China’s Compute Catch-Up
The $295 billion Chinese data center buildout, running on domestic Huawei Ascend chips and domestic alternatives, reduces the compute gap faster than US export controls can compensate for. If China achieves meaningful compute parity by 2028 to 2029, the benchmark convergence already underway (from 17.5 percentage points behind on MMLU in 2023 to 0.3 points by end of 2024) combines with patent volume and deployment scale to create genuine strategic dominance. The chip export control strategy, which is currently doing more strategic work than any AI law, then becomes the most consequential regulatory decision of the 2020s, and the question becomes whether it held long enough.
Scenario D: The Innovation-Safety False Choice Resolves Badly
The Stanford 2026 AI Index documents 362 AI incidents in 2025, up from 233 in 2024. The report’s assessment is direct: “Responsible AI is not keeping up with AI capability.” The US deregulatory bet is a wager that no major consumer harm event occurs before political will develops to legislate properly. If a high-profile harm event happens in 2026 or 2027, the post-incident legislation will be rushed, punitive, and poorly designed. Reactive AI governance is almost always worse than proactive governance on any metric that matters for long-term innovation.
Frequently Asked Questions
What is the EU AI Act and when does it take effect?
The EU AI Act (Regulation 2024/1689) is the world’s first comprehensive, binding AI law. It entered into force August 1, 2024. Prohibited AI practices have been enforceable since February 2025. High-risk AI system obligations covering hiring, biometrics, credit scoring, law enforcement tools, medical diagnostics, and education assessment take full effect August 2, 2026, with penalties up to €35 million or 7% of global annual revenue.
How does the US regulate AI compared to the EU?
The US has no comprehensive federal AI law as of June 2026. It regulates AI sector-by-sector through agencies including the FTC, FDA, EEOC, and CFPB. President Trump’s January 2025 executive order explicitly removed prior safeguards to prioritize innovation speed and directed the DOJ to challenge state-level AI laws. The EU, by contrast, uses a single risk-based framework with binding rules and major fines applying to any company serving EU users regardless of where they’re headquartered.
How many AI patents does China have?
According to WIPO’s Patent Landscape Report on Generative AI (July 2024), China-based inventors filed 38,210 generative AI patents between 2014 and 2023, more than six times the US total of 6,276. China accounts for 49.1% of all global patent applications in 2024. However, China’s GenAI patent grant ratio is approximately 32%, and most patents lack international PCT protection, limiting enforceability outside China.
Is China winning the AI race?
It depends on the metric. China leads in patent volume, AI publications, and industrial robot deployment, and has nearly closed the model quality gap to just 2.7% behind the US as of March 2026. But the US leads in private AI investment ($285.9 billion in 2025 versus China’s $12.4 billion), compute power (US holds 50% of global AI compute versus China’s 400,000 petaflops), and frontier model production (40 notable models in 2024 versus China’s 15).
What are the penalties for violating the EU AI Act?
EU AI Act penalties are tiered by violation type. Deploying prohibited AI systems (such as social scoring or untargeted biometric scraping) carries fines up to €35 million or 7% of global annual turnover. High-risk system violations carry fines up to €15 million or 3% of turnover. Providing incorrect information to regulators can result in fines up to €7.5 million or 1% of turnover. These maximums exceed GDPR’s penalty structure across all categories.
Does the EU AI Act apply to US companies?
Yes. The EU AI Act has extraterritorial reach identical in structure to GDPR. It applies to any organization placing AI systems on the EU market or producing AI outputs used by EU residents, regardless of where the company is headquartered or where the AI system runs. A US firm using AI for credit decisions or hiring screening that serves European customers falls within scope even if all infrastructure is based in the US.
What is the Brussels Effect in AI regulation?
The Brussels Effect, documented by Columbia Law professor Anu Bradford, describes how EU regulations become de facto global standards because it’s operationally more efficient for multinationals to comply with the strictest framework universally than to maintain separate regional versions. In AI, Adobe and OpenAI have globally embedded C2PA watermarking standards (an EU Article 50 requirement) rather than building EU-only compliance infrastructure. The EU required it; the rest of the world adopted it.
What AI systems does China regulate?
China regulates AI through a layered stack of sectoral laws: algorithm recommendation rules effective March 2022, deepfake and synthetic media rules effective January 2023, generative AI interim measures effective August 2023 (the world’s first binding GenAI law), and Cybersecurity Law amendments effective January 2026. Generative AI services must register with China’s Cyberspace Administration of China, pass security assessments, use legally sourced training data, and ensure content alignment with “socialist core values.” Non-compliance can mean service suspension or loss of operating license.
The Bottom Line
No single jurisdiction is winning the AI regulation race in 2026. But the question of who’s winning obscures the more important question: is any of the three approaches actually adequate for what’s coming?
The US is winning private capital and compute infrastructure while betting that catastrophic failure doesn’t arrive before political will does. The EU is winning the standards race while producing almost nothing with the technology it’s regulating. China is winning deployment scale and benchmark convergence while facing a hardware constraint that could define the next five years.
The most honest read is Neuwirth’s: the race framing is itself the problem. It encourages bad regulatory timing, obscures deeper commonalities between approaches, and makes cooperation harder at exactly the moment when a cross-border AI incident would demand it. The first genuinely catastrophic AI event will expose every gap in all three frameworks simultaneously. Right now, no jurisdiction has a clear liability protocol for that scenario. All three will be pointing fingers.
For practitioners: treat August 2, 2026 as binding regardless of the Digital Omnibus outcome. Build EU-standard compliance globally, run a separate China compliance track, and don’t mistake federal deregulation in the US for immunity from state-level or extraterritorial exposure.
Three things to watch over the next eighteen months. First, whether the EU AI Office’s first major GPAI fine triggers a political response from the US administration that accelerates market fragmentation. Second, whether the Huawei Ascend chip program reduces China’s compute disadvantage faster than the export control architecture anticipated. Third, whether the rate of AI incidents (362 documented in 2025, up 55% from 2024) produces a consumer harm event large enough to force reactive US federal legislation before the midterm cycle.
The regulation race isn’t over. But the shape of who wins it is clarifying fast. And the regimes that fail to cooperate when the first cross-border incident hits will be writing the most consequential AI policy of the decade, just not the kind they intended.
The Neural Loop covers AI regulation, enterprise AI, and tech policy every week. No noise. No filler. Just what matters to practitioners.
Subscribe to The Neural Loop
Your Cloud Is Misconfigured Right Now. 82% of Enterprises Are. AI Found the Gaps in 14 Minutes That Manual Audits Missed for 8 MonthsCloud Security • AI • Enterprise
Your Cloud Is Misconfigured Right Now. 82% of Enterprises Are. AI Found the Gaps in 14 Minutes That Manual Audits Missed for 8 Months
By NeuralWired Editorial Team • June 23, 2026 • 14 min read
On January 7, 2025, a researcher discovered that DeepSeek, one of the most talked-about AI companies on the planet, had left a database completely open to the public internet. No password. No authentication. No encryption. Over one million user records, including chat histories, API keys, and backend credentials, were sitting exposed. The breach didn’t require a sophisticated attack. It required a browser and a URL. DeepSeek suspended global signups the same day.
This wasn’t a nation-state operation. It wasn’t a zero-day exploit. It was a cloud misconfiguration, and it took less than a minute to exploit once discovered. The irony of an AI company being undone by something an AI tool would have caught in seconds was not lost on the security community.
Now consider this: DeepSeek’s misconfiguration almost certainly existed for weeks or months before anyone found it. That’s not unusual. According to compiled research from DataStackHub published in May 2026, the average detection time for a cloud configuration issue exceeds 180 days. Not 180 hours. Not 180 minutes. A hundred and eighty days. For context, that’s the time it takes for summer to turn to winter. Your cloud environment can be leaking data from one season to the next before a human reviewer notices anything is wrong.
AI-powered cloud security tools compress that window to minutes. The gap between those two realities is where this article lives.
The Silent Epidemic: Cloud Misconfiguration Is the #1 Enterprise Security Risk
The Cloud Security Alliance surveyed over 500 cloud security practitioners for its Top Threats to Cloud Computing 2024 report. Misconfiguration and inadequate change control ranked first. Not ransomware. Not nation-state intrusion. Not zero-day vulnerabilities. A mistyped setting. A forgotten public access toggle. An IAM policy that’s slightly too permissive.
Gartner put a sharper number on it years ago, and the finding has only grown more cited: through 2025, 99% of cloud security failures were the customer’s fault, primarily due to misconfigurations. The cloud platform didn’t fail. The configuration of it did.
When you ask where these errors come from, the answer is frustratingly human. DataStackHub’s compiled analysis of cloud misconfiguration statistics, published May 2026, found that 82% of cloud configuration errors originate from manual setup or human oversight. Engineers working fast. Scripts without peer review. Infrastructure spun up in a sprint that nobody went back to audit. The cloud didn’t create this problem. The pace of cloud adoption did.
The numbers compound. Ninety percent of enterprises report at least one cloud security incident annually. Sixty-five percent experienced at least one incident in the past 12 months, up from 61% the year prior, according to a Cybersecurity Insiders survey of 937 CISOs and security professionals conducted in early 2025. The trajectory is not improving.
“Cybersecurity is facing a unique moment, where AI-enhanced threat intelligence, products, and services have begun to give defenders an advantage over the threats they face that had proven elusive, until now.”
Nick Godfrey, Senior Director, Office of the CISO, Google Cloud (Cloud CISO Perspectives, December 2025)
The reason this problem has stayed hidden so long is structural. Cloud infrastructure scales exponentially. Security governance doesn’t. An engineering team can provision hundreds of new cloud resources in a single afternoon. The security team is still reviewing last quarter’s audit.
The Numbers That Should Keep You Up at Night
180+
Days average detection time without automation
72 hrs
Median time from vulnerability disclosure to exploitation
$4.44M
Global average cost of a data breach (IBM 2025)
136%
Growth in cloud intrusions, H1 2025 vs all of 2024
Put those four numbers next to each other and the arithmetic is brutal. Attackers move from discovering a vulnerability to exploiting it in 72 hours. Your organization, on average, won’t detect the resulting cloud configuration issue for 180 days. That’s not a detection gap. It’s a six-month open window.
The financial damage follows predictably. IBM’s 2025 Cost of a Data Breach Report, conducted by the Ponemon Institute across 604 organizations in 17 countries, puts the global average breach cost at $4.44 million. In the United States, that number climbs to $10.22 million. Multi-environment breaches spanning cloud and on-premises infrastructure cost the most at $5.05 million. These aren’t projections. They are activity-based cost calculations from real breach events between March 2024 and February 2025.
Metric
Manual Audit
AI-Powered CSPM
Average detection time
180+ days
Real-time to minutes
Detection time reduction
Baseline
40%+ faster in mature environments
Mean time to detect (SOC)
Baseline
45-55% reduction (AI-enhanced SOCs)
Breach containment time
~80 days
~40 days
Average breach cost impact
Full exposure
$1.9M savings per breach (IBM 2025)
Breach lifecycle
Baseline
80 days shorter (IBM 2025)
Organizations detecting within 1 hour
9%
Up to 60%+ with AI monitoring
Coverage frequency
Quarterly or annual
Continuous, 24/7
The alert volume problem is a separate dimension of the same crisis. Large enterprises receive an average of 3,000 or more configuration alerts per month, with 40% of all security dashboard alerts relating to misconfigured assets (DataStackHub, 2026). No security team can manually triage 3,000 alerts monthly while also doing everything else the job requires. The math makes manual review not just inefficient but mathematically impossible at enterprise scale.
Meanwhile, CrowdStrike’s 2025 Threat Hunting Report documented something that should recalibrate every enterprise security budget conversation: cloud intrusions in the first half of 2025 grew 136% compared to the entirety of 2024. Attackers have automated their cloud reconnaissance. They are scanning for exposed assets faster than most organizations are generating the alerts to notice.
The Manual Audit Is Already Dead. The Market Just Hasn’t Admitted It Yet.
Toyota learned this in 2023. A misconfigured cloud storage bucket exposed 260,000 customer records. The error was described at the time as “a rather low-profile and fairly straightforward mistake with a gigantic impact.” Toyota is not a company short on engineering talent. The mistake happened anyway because manual configuration at scale is a process, and processes fail.
Capital One learned it in 2019, when a misconfigured AWS Web Application Firewall enabled access to over 100 million customer records. The regulatory fine from the OCC was $80 million. The class action settlement reached $190 million. That single misconfigured rule cost the company more than a quarter billion dollars and defined the boardroom conversation about cloud security for years afterward.
The pattern repeats because the root cause never changes: manual configuration at cloud speed is structurally broken. Three forces made this inevitable.
Cloud Adoption Speed Outpaced Security Governance
The ability to provision cloud infrastructure in minutes created a permanent structural gap with security teams still operating on quarterly review cycles. By the time a manual audit catches a misconfigured security group, that group may have been exploitable for two business quarters.
Multi-Cloud Complexity Multiplied Exposure
Gartner reports that 76% of enterprises now use at least two cloud providers, and 69% use three or more. AWS, Azure, and Google Cloud have different IAM models, different security terminology, and different default configurations. A configuration that’s correct on one platform can be dangerously permissive on another. Security teams managing multi-cloud environments are expected to hold three overlapping mental models simultaneously while working under constant deployment pressure.
47% of Developers Still Deploy Infrastructure Manually
DataStackHub’s 2026 research found that 47% of developers deploy infrastructure manually at least once per month. Every manual deployment is a potential misconfiguration event. Every potential misconfiguration event, without continuous monitoring, is a gap that could sit undetected for months.
Key Context
The 54% of cloud environments that contain credentials hard-coded in configuration files or containers are not edge cases or outliers. They are the documented default state of most enterprise cloud environments operating without automated configuration governance.
To understand why this matters at speed, consider the exploitation timeline. DataStackHub’s cloud vulnerability statistics show that 37,000 or more new vulnerabilities were published in 2025, a 22% increase from 2024. The median time from vulnerability disclosure to active exploitation in cloud environments is 72 hours. Organizations running manual audits on 180-day cycles are patching vulnerabilities that attackers began exploiting three months ago.
What AI-Powered CSPM Actually Does (And How to Tell If a Vendor Actually Has It)
Cloud Security Posture Management, or CSPM, is a category of tools that continuously scan cloud environments for misconfigurations, compliance gaps, and security risks across AWS, Azure, and Google Cloud. The category has existed for years. What changed in 2024 and 2025 is the depth of AI integration and, more importantly, the sophistication of what that AI is actually doing.
The meaningful divide in the market today isn’t between CSPM tools that detect and tools that don’t. Most of them detect. The divide is between tools that flag individual misconfigurations and tools that model attack paths: chains of misconfigurations that, individually, might score as medium severity but, combined, create a direct path to your crown jewels.
Attack Graph Analysis vs. Rule-Checking
Traditional CSPM tools operate like code linters: they check your configuration against a list of known-bad rules and flag violations. This is useful. It is not sufficient. A mature AI-powered CSPM platform builds a graph of your entire cloud environment, maps relationships between every resource and permission, and then reasons about which combinations of flaws create exploitable paths to critical data. That’s a qualitatively different capability, and it’s the one that compresses detection from months to minutes.
IaC Scanning in CI/CD Pipelines
The most effective deployment shifts security left: embed CSPM scanning into infrastructure-as-code templates before any code reaches production. A misconfigured security group caught in a pull request costs seconds to fix. A misconfigured security group caught six months after deployment may have cost millions. Tools like Tenable, Palo Alto Prisma Cloud, and Wiz support IaC scanning natively, allowing DevSecOps teams to enforce configuration policy at the point of creation.
Agentless Deployment: The Path of Least Resistance
One of the adoption barriers for earlier CSPM tools was deployment complexity. Modern platforms have largely solved this through agentless architecture: they connect directly to cloud provider APIs without requiring agent installation on individual workloads. Wiz’s agentless model is widely credited as one of the reasons it became the fastest-growing cybersecurity company in history before Google’s acquisition. Zero agent installation means full coverage can be achieved in hours rather than weeks.
“Architecture beats features. An AI bolted onto a weak security foundation won’t save you. If identity is broken, data governance is unclear, or network visibility is fragmented, AI simply operates on bad inputs and produces unreliable outputs.”
CISO practitioner perspective, compiled by Computer Weekly, January 10, 2026
The “AI Washing” Warning Every Buyer Needs to Hear
Here is where the critical perspective matters. A Computer Weekly analysis published in January 2026, drawing on practitioner community input, documented a significant “AI washing” problem in the CSPM vendor market. Vendors routinely rebrand traditional rule-based heuristics as “AI-powered” without meaningful machine learning sophistication behind the label.
Buyer Alert
Before signing any CSPM contract, ask the vendor four hard questions: What specific ML model underlies the detection capability? How frequently is it retrained on new threat data? What is the documented false positive rate at enterprise scale? And what is the escalation path when the AI is wrong? Vendors who can’t answer these questions clearly are selling rules-based tools with an AI marketing wrapper.
The Lacework trajectory makes this concrete. The company raised $1.8 billion at an $8.3 billion peak valuation partly on AI-capability claims. In August 2024, Fortinet acquired it for an estimated $200 to $230 million. The market found that AI-capability marketing doesn’t always translate to durable AI-capability value.
The Regulatory Hammer Has Landed: CISA BOD 25-01 and NIS2
On December 17, 2024, CISA issued Binding Operational Directive 25-01, requiring every Federal Civilian Executive Branch agency in the United States to secure its cloud environments using SCuBA (Secure Cloud Business Applications) configuration baselines. This wasn’t a recommendation. It was a legal mandate with hard deadlines: identify all cloud tenants by February 21, 2025; deploy SCuBA automated assessment tools by April 25, 2025; implement all mandatory policies by June 20, 2025.
“The configurations that this BOD requires are not specific to any threat actor or incident. They are used consistently by both sophisticated, well-funded threat actors and common cybercriminals.”
Matt Hartman, Deputy Executive Assistant Director for Cybersecurity, CISA (Federal News Network, December 17, 2024)
Hartman’s framing is the clearest statement in recent government cybersecurity history about why cloud misconfiguration is a universal attack vector rather than an advanced threat problem. The nation-state hackers and the script-kiddie opportunists are both scanning for the same exposed storage buckets and over-permissioned IAM roles. Sophistication of the attacker doesn’t change the exploitability of the target.
The BOD’s lineage traces directly to SolarWinds. CISA began developing the SCuBA baseline framework in the aftermath of the 2020 supply chain campaign that exploited configuration gaps in cloud email and collaboration environments used by federal agencies. BOD 25-01 is the mandated formalization of lessons learned from one of the most damaging cyberattacks in U.S. government history.
For private sector organizations, BOD 25-01 is not legally binding. But it is directionally definitive. Regulatory frameworks in regulated industries, from financial services to healthcare, consistently follow federal cybersecurity mandates with a lag of 12 to 24 months. If your organization touches federal contracts or operates in a regulated sector, the question is not whether these requirements will reach you but when.
In Europe, the NIS2 Directive, adopted in October 2024, mandates stricter risk management and incident reporting obligations for organizations operating cloud computing infrastructure across EU member states. Together, BOD 25-01 and NIS2 represent the first coordinated transatlantic regulatory push to formalize cloud misconfiguration detection as a compliance requirement rather than a best practice.
What the Skeptics Get Right (And What They Miss)
This article would be incomplete without an honest accounting of what AI-powered cloud security doesn’t solve. The critical perspective isn’t a footnote. It’s load-bearing.
Alert Fatigue May Get Worse Before It Gets Better
A CSPM tool that generates 3,000 alerts per month in a large enterprise doesn’t automatically solve the problem. It can reproduce the same gap at higher visibility if the organization lacks the DevSecOps infrastructure to triage and remediate in priority order. A 2024 analysis found that 91% of organizations experience security blind spots when using fragmented cloud security tools (AccuKnox, February 2026). Detection capability without a mature remediation workflow is a louder version of the same silence.
The differentiator here is intelligent prioritization. CSPM tools that score alerts purely on configuration deviation are generating noise. Tools that rank alerts by exploitability, attack path severity, and proximity to sensitive data are generating signal. The buying decision has to account for this distinction.
Attackers Use AI Too
The IBM 2025 Cost of a Data Breach Report documented a finding that deserves more attention than it’s received: 1 in 6 breaches in the study period involved attackers using AI, most commonly for phishing (37%) and deepfake impersonation (35%). The same AI capabilities that enable CSPM platforms to scan cloud environments faster are being used by attackers to find and exploit misconfigurations faster.
Rich Mogull, Chief Analyst at the Cloud Security Alliance, co-authored a CISO playbook in April 2026 that frames this precisely:
“Time-to-exploit has collapsed from 2.3 years in 2018 to under one day in 2026. AI didn’t start this trend, but it is accelerating it beyond what current patch cycles can absorb. Static, manual defenses are structurally obsolete.”
Rich Mogull, Chief Analyst, Cloud Security Alliance (CSA AI Vulnerability Storm CISO Playbook, April 2026)
AI-powered CSPM shifts the detection speed race significantly in defenders’ favor. It doesn’t end the race. Organizations still need to close the gap between detection and remediation, and that gap requires human judgment about business context that AI systems still don’t fully possess. (For a look at how automated remediation pipelines are evolving, NeuralWired’s coverage of AIOps self-healing infrastructure goes deeper on what comes after detection.)
Governance Can’t Be Automated Away
DataStackHub’s 2026 analysis found that 31% of teams lack standardized configuration templates or baselines. IBM’s 2025 breach report found that 63% of breached organizations had no AI governance policy in place. Shadow AI tools used by employees without organizational authorization added an average of $670,000 to breach costs in IBM’s dataset.
Tools without governance are inputs without outputs. The most sophisticated CSPM platform in the world produces unreliable results if the underlying cloud architecture has broken identity controls, unclear data ownership, or fragmented network visibility. The Computer Weekly practitioner community put this plainly: “Architecture beats features.” That’s not skepticism of AI. That’s a prerequisite for it.
The CSPM Market Reality: Where the Money Is Going
Markets vote with capital, and capital has a clear view on this problem. Gartner’s Information Security Market Current Outlook published in March 2026 named CSPM the single fastest-growing security category globally, with a 31.23% compound annual growth rate. The CSPM market was valued at $4.7 billion in 2025 and is projected to reach $16.2 billion by 2030. Independent research from Fortune Business Insights projects even higher growth, estimating the market reaches $21.31 billion by 2034.
Worldwide end-user spending on information security reached $213 billion in 2025 and is forecast to climb to $244 billion in 2026, a 13.3% increase. Within that total, cloud security is the fastest-growing subsegment at 28.8% year-over-year growth (Gartner, July 2025).
The Platform Consolidation Story
Google’s acquisition of Wiz, completed in Q1 2026, signals that CSPM has graduated from third-party tool to hyperscaler-level competitive priority. Wiz now integrates natively with Google Cloud’s security stack and supports multi-cloud environments spanning Databricks, AWS Agentcore, Azure Copilot Studio, and Salesforce Agentforce. At Google Cloud Next in April 2026, Google announced an AI-native Threat Hunting agent capable of proactively identifying novel attack patterns, extending CSPM from reactive detection to active hunting.
Microsoft Defender for Cloud has similarly expanded its multi-cloud CSPM coverage. Palo Alto Networks’ Prisma Cloud and Tenable round out the enterprise tier. Orca Security and Lacework (now under Fortinet) serve mid-market and specialized needs. The market is consolidating around platforms, not point tools.
Our read: the Google-Wiz integration in particular changes the competitive calculus for enterprises already standardized on Google Cloud. CSPM isn’t an add-on purchase anymore. It’s a default capability of the platform. For organizations on AWS or Azure, that means evaluating whether native CSPM from their hyperscaler or a best-of-breed independent tool better fits their environment. The answer depends heavily on multi-cloud complexity, not just feature comparison.
NeuralWired’s earlier reporting on AI-powered vulnerability discovery explores how the most advanced AI security capabilities are being deployed at the frontier, providing additional context for where enterprise CSPM is heading over the next 18 months.
What CISOs and CTOs Should Do This Week
The research case is complete. Here is the operational translation.
For CISOs
Run a cloud tenant inventory now. If you don’t have a complete, current list of every cloud account across every provider, you can’t protect what you can’t see. CISA BOD 25-01 required federal agencies to complete this step by February 2025. If you haven’t, you are behind the regulatory baseline.
Deploy continuous monitoring, not quarterly audits. The 180-day detection average isn’t a technology problem, it’s a process architecture problem. Continuous CSPM monitoring is the architectural fix. A quarterly audit schedule is structurally incompatible with a 72-hour exploitation window.
Demand attack-path analysis, not just alert counts. When evaluating CSPM vendors, the relevant capability is not how many misconfigurations the tool detects. It is whether the tool can show you which combinations of misconfigurations create an exploitable path to critical assets. That’s the difference between 3,000 alerts and three critical priorities.
Address misconfigured identity policies first. DataStackHub’s 2026 analysis found that misconfigured identity policies are responsible for 1 in 3 cloud breaches. Valid account abuse is the leading initial access tactic in 35% of cloud incidents (CrowdStrike 2025). IAM misconfiguration is the highest-value target for both your CSPM coverage and your remediation queue.
Build a governance layer around your AI tools. IBM 2025 found that 63% of breached organizations had no AI governance policy. Shadow AI tools used without organizational authorization added $670,000 per incident to breach costs. The AI security tools themselves need governance frameworks. For a structured approach to this, NeuralWired’s coverage of enterprise AI risk management frameworks provides the NIST-aligned baseline.
For CTOs and Cloud Architects
Embed IaC security scanning in every CI/CD pipeline. Infrastructure-as-code is how misconfigurations get created at speed. It’s also where they’re cheapest to catch. Require IaC security scanning as a mandatory gate in your deployment pipeline, not an optional review step.
Define a configuration baseline and enforce drift detection. Every cloud resource should have a documented acceptable configuration state. Any deviation from that state should trigger an alert automatically. Without a defined baseline, your CSPM tool is generating alerts against no standard, and remediation teams have no clear target state to restore.
Stop deploying infrastructure manually. Forty-seven percent of developers still make manual infrastructure deployments monthly. Each one is a potential misconfiguration that bypasses your scanning pipelines. Every manual deployment should require security review or be eliminated from the workflow entirely. For the broader architectural picture, NeuralWired’s enterprise hybrid cloud strategy coverage addresses how AI workload placement and security governance intersect.
For CIOs and Board-Level Executives
The financial case in simplified form: the average U.S. breach costs $10.22 million. AI-powered CSPM tools reduce that exposure by $1.9 million per breach on average. CSPM platforms at the enterprise level run at a fraction of that cost annually. The ROI calculus closes with a single prevented incident.
By 2026, estimates suggest 20 to 25% of total IT budgets will be allocated to cloud security. Organizations not scaling security investment proportionally to their cloud infrastructure investment are building exposure faster than they’re building coverage. That gap is what breaches cost.
Frequently Asked Questions
What is cloud misconfiguration?
A cloud misconfiguration is a security error caused when a cloud resource, such as a storage bucket, IAM policy, network security group, or database, is configured incorrectly, leaving it exposed to unauthorized access or attack. The Cloud Security Alliance ranks it the number one cloud security threat, and Gartner analysis shows misconfigurations account for 99% of cloud security failures through 2025.
How long does it take to detect a cloud misconfiguration?
Without automation, the average detection time for a cloud configuration issue exceeds 180 days, according to 2026 research. Some organizations without automated tools don’t detect cloud breaches for 219 days on average. AI-powered CSPM tools reduce detection time by more than 40% in mature environments and can identify misconfigurations continuously in real time rather than through periodic manual audits.
What percentage of enterprises have cloud misconfigurations?
Research shows over 90% of enterprises experienced at least one cloud security incident annually, with misconfiguration as the leading cause. According to multiple analyst studies, 82% of cloud configuration errors originate from manual setup and human oversight, meaning nearly every enterprise relying on manual configuration practices carries active misconfiguration risk at any given moment.
How much does a cloud misconfiguration breach cost?
The global average cost of a data breach is $4.44 million in 2025 according to IBM’s Cost of a Data Breach Report, conducted across 604 organizations by the Ponemon Institute. In the U.S., the average reaches $10.22 million. Multi-environment breaches spanning cloud and on-premises environments cost the most at $5.05 million. Organizations using AI-powered detection save an average of $1.9 million per breach.
What is CSPM (Cloud Security Posture Management)?
CSPM is a category of tools that continuously monitor cloud environments for misconfigurations, compliance gaps, and security risks across AWS, Azure, and Google Cloud. Unlike periodic audits, CSPM tools scan 24/7 using AI and automation, comparing configurations against frameworks such as CIS Benchmarks, SOC 2, and NIST. The CSPM market is the fastest-growing security category globally, with 31% annual growth according to Gartner’s 2026 forecast.
What is CISA BOD 25-01?
CISA Binding Operational Directive 25-01, issued December 17, 2024, requires all U.S. Federal Civilian Executive Branch agencies to identify cloud tenants, deploy automated security assessment tools called SCuBA, and implement mandatory cloud configuration baselines. Deadlines ran through June 20, 2025. CISA strongly recommends all organizations, not just federal agencies, adopt the same cloud security practices.
Can AI detect cloud misconfigurations better than manual audits?
Yes. AI-powered CSPM tools continuously scan cloud environments in real time, while manual audits typically occur quarterly or annually. IBM research shows organizations using AI in security contain breaches 80 days faster and save $1.9 million per breach on average. AI-enhanced SOCs reduce mean time to detect by 45 to 55%, compressing what takes humans months into detection windows measurable in minutes.
What causes cloud misconfigurations?
The primary causes are manual setup (82% of errors originate from human oversight), lack of standardized configuration templates (31% of teams have none), poor change management practices, and rapid cloud deployment speeds that outpace security governance. Multi-cloud complexity across AWS, Azure, and GCP multiplies the risk, as each provider uses different IAM models, security controls, and terminology that teams must manage simultaneously.
Where This Goes in the Next 18 Months
The cloud misconfiguration problem is not going away. It’s accelerating. CrowdStrike documented 136% growth in cloud intrusions in the first half of 2025 alone. The exploitation window has collapsed from years to hours. The average enterprise is operating with configurations that haven’t been reviewed in six months and attackers who’ve already automated the search for the ones that matter.
What changes in the next 18 months is the capability boundary of the defenders. Google’s Threat Hunting agent, announced at Google Cloud Next in April 2026, represents a shift from reactive CSPM to proactive threat hunting: AI systems that don’t just flag known-bad configurations but actively search for novel attack patterns before they’re exploited. That’s a qualitatively different class of tool, and it’s arriving in enterprise preview now.
Three things to watch: First, whether regulatory frameworks cascade from BOD 25-01 into financial services and healthcare compliance requirements over the next 12 months. Second, whether the CSPM market consolidates further around hyperscaler-native platforms or whether independent specialists maintain competitive differentiation on attack-path analysis depth. Third, and most important, whether organizations close the gap between detection and remediation, because the tools to find misconfigurations faster are outpacing the organizational capacity to fix them.
The manual audit had its era. That era is over. The organizations that accept that reality and deploy continuous AI-powered cloud security monitoring now will contain their next breach in 40 days. The ones that don’t will spend the better part of a year finding out they’ve been exposed.
Stay Ahead of the Threat Curve
Get NeuralWired’s weekly intelligence briefing on AI, cybersecurity, and enterprise technology. Trusted by CISOs, CTOs, and cloud architects across the U.S., UK, Canada, Europe, and Australia.
Subscribe to The Neural Loop
AI SOC Automation: How AI Closed 43% of Alerts Before a Human Saw Them — and What the 2% Failure Rate Actually Cost | NeuralWiredSecurity Operations • Enterprise AI
AI SOC Automation Closed 43% of Alerts Before a Human Saw Them. Here’s What Lived Inside the 2% It Got Wrong.
By NeuralWired Research Desk • June 22, 2026 • 12 min read
Every weekday morning, a real threat is hiding inside a low-severity alert at the average enterprise. The AI already looked at it. The AI already closed it. The analyst never saw it.
That is not a hypothetical from a vendor white paper. It is a finding from Intezer’s 2026 AI SOC Report, which analyzed 25 million security alerts across live enterprise environments in 2025, performed 82,000 forensic endpoint memory scans, and found that nearly 1 percent of all confirmed incidents originated from alerts the security stack had labeled low-severity or informational. At a typical enterprise receiving 450,000 alerts per year, that works out to roughly 54 real threats annually hiding in the deprioritized backlog. One per week. Every week.
The AI SOC automation story being told across the industry right now is mostly good news. Platforms are reaching 98 percent triage accuracy. Analysts are getting 40-plus hours of manual work back every week. Breach containment timelines are shrinking by 80 days. All of that is real and documented. But the 2 percent that gets wrong deserves a much harder look than it is currently receiving, because of what is specifically in that error tail.
This article unpacks what the primary data actually shows, explains the governance framework that leading CISOs are building around it, and names the failure modes that almost no vendor is talking about publicly.
The Numbers Behind the Headline
The 43 percent figure in the headline sits comfortably within the documented range of AI triage automation rates across real enterprise deployments. It is a representative midpoint, not a single published statistic. Here is what the primary data actually shows:
>98%Triage accuracy for CrowdStrike Charlotte AI, measured against Falcon Complete MDR expert decisions
<2%Of 25 million enterprise alerts escalated to human analysts in Intezer’s 2026 dataset
61%Reduction in analyst alert queue from AACT academic system across 3.1 million live SOC alerts
The problem these platforms are solving is genuine and severe. Enterprise SOCs now receive between 3,000 and 10,000 security alerts per day. Between 40 and 63 percent of those alerts go completely uninvestigated in traditional setups. Ninety percent of the ones that do get investigated turn out to be false positives. The global cybersecurity workforce gap sits at 4.8 million unfilled positions, growing at 19 percent year-over-year. Seventy-one percent of SOC analysts report burnout. Sixty-four percent say they are considering leaving within a year.
The human model of alert triage is structurally broken. AI SOC automation is not an efficiency preference at this point. For most enterprises, it is an operational necessity.
CrowdStrike Charlotte AI, which reached general availability in February 2025, eliminates more than 40 hours of manual triage per week per analyst team and operates under what CrowdStrike CTO Elia Zaitsev calls “bounded autonomy.” The system does not act unilaterally. Customers define exactly when and how the AI acts, and the model was trained on millions of real triage decisions made by Falcon Complete MDR experts.
“Different organizations are going to have different levels of skepticism and different risk tolerances. One of the nice things, because of the way we’ve integrated [Charlotte AI] with the automation system, is our customers actually get to determine, by taking advantage of this Fusion integration, where, when and how you trust the system.”
Elia Zaitsev, Chief Technology Officer, CrowdStrike — VentureBeat, February 2025
The IBM Cost of a Data Breach Report 2025 (Ponemon Institute, 600 organizations across 17 industries and 16 countries) quantifies what that accuracy buys: organizations using AI and automation extensively see an average breach cost of $3.62 million versus $5.52 million for those with no AI. That is a $1.9 million per-breach saving. AI also cut breach lifecycles by 80 days compared to organizations without it. Thirty-two percent of organizations are now using security AI and automation extensively, up from 31 percent in 2024.
The efficiency case is not in dispute. The governance case is where things get complicated.
What Actually Lives Inside the 2% Error Rate
When an AI SOC system reports 98 percent accuracy, the immediate question any serious CISO should ask is: what is specifically in the 2 percent? Not in aggregate. Not blended with false positives that just wasted analyst time. What threats specifically are being missed?
Intezer’s forensic data answers this with uncomfortable precision.
Of the 82,000 endpoints that underwent live forensic memory scans in Intezer’s 2025 dataset, 2,600 had active infections. That alone is significant. But the finding that should change how every enterprise thinks about AI triage closure is this: 51 percent of those confirmed compromised endpoints had already been marked “mitigated” by the source EDR vendor. The machine had been declared clean. It was not clean.
The malware families found active in memory on those “mitigated” endpoints were not proof-of-concept tools or research artifacts. They were Mimikatz, Cobalt Strike, Meterpreter, and StrelaStealer. These are active criminal and nation-state workhorses. They were sitting in memory, on machines that the security stack had officially declared safe, in environments where the AI was using EDR verdict as an input signal for closure decisions.
Critical Finding
1.6 percent of all forensic endpoint scans in Intezer’s 2026 dataset found active compromise despite EDR reporting “mitigated.” The AI did not invent the error. It inherited it from a flawed upstream input. This is the operational gap most AI SOC deployments are not designed to catch.
This is a layered failure. The EDR declared the machine clean. The AI received that verdict as a trusted data point. The AI closed the alert. No human ever reviewed it. Cobalt Strike stayed in memory.
Itai Tevet, CEO and co-founder of Intezer and former head of IDF cyber incident response, frames what this finding demands of security leadership:
“Security teams have normalized the idea that some risk must be accepted because it is impossible to investigate everything. Our research shows that this acceptance is increasingly misaligned with how modern attacks unfold. When genuine threats consistently emerge from alerts we have trained ourselves to ignore, the definition of acceptable risk needs to be reexamined.”
Itai Tevet, CEO, Intezer — GlobeNewswire, February 3, 2026
The peer-reviewed academic data reinforces this picture from a different angle. The AACT system (Automated Alert Classification and Triage), deployed in a real managed SOC environment across 3.1 million live alerts over six months, achieved a false negative rate of 1.36 percent. That sounds small. At 3 million alerts, it represents 40,800 real threats that the system incorrectly closed. The precision of that number matters: it came from an independently published, peer-reviewed academic paper using actual production SOC data, not vendor-reported customer telemetry.
At an enterprise receiving 10,000 alerts per day, a 2 percent blended error rate produces 200 wrong dispositions every single day. The critical question is whether those errors skew toward false positives (wasted time) or false negatives (missed threats). That calibration is not set by the AI vendor. It is a policy decision that the deploying organization must make explicitly, before deployment, based on its own risk tolerance.
When AI Automation Attacks Its Own Network
The failure mode that nobody wants to include in their AI SOC pitch deck happened at a real enterprise, and the documentation is on record.
An enterprise AI-driven SOC response system was programmed to automatically isolate endpoints showing signs of compromise. A software update triggered false positives across hundreds of devices simultaneously, including critical production servers. The AI executed correctly according to its programming. It locked every flagged endpoint. The result was a self-inflicted denial-of-service attack on the organization’s own production infrastructure.
The root cause investigation found something more troubling than a simple misconfiguration. Over time, the AI had been trained to ignore certain low-level anomalies that had repeatedly proved benign. That created a model drift blind spot. When new attack patterns emerged that resembled previously-benign behavior, the system missed them. The same suppression mechanism that reduced false positives also lowered the detection threshold for real threats that looked familiar.
This is the automation complacency trap, and it is not unique to security AI. A 2024 peer-reviewed study from ETH Zurich found that human-in-the-loop designs increase uptake of AI recommendations but decrease overall accuracy. Participants were statistically less likely to intervene on the AI’s least accurate recommendations. The implication is that human oversight can create a false sense of verification without actually catching the errors it is supposed to catch.
Key Insight
Stale training data is now the leading cause of false positive spikes in AI SOC tools, according to the SANS 2025 SOC Survey. A system tuned to eliminate false positives compensates by raising its detection threshold, which also suppresses low-signal real threats. Attackers learn to look boring. The AI learns to ignore boring. This is not a theoretical concern. It is a documented, measurable attack surface.
Vectra AI’s 2026 State of Threat Detection research found that 40 to 63 percent of alerts still go uninvestigated at organizations running traditional setups, and that stale model data is the primary driver of false positive inflation in AI-augmented environments. The AI SOC solves the volume problem. Model drift creates a new version of the coverage problem.
There is no industry standard for AI model drift monitoring in SOC deployments. ISO/IEC 42001, the December 2023 global standard for AI management systems, requires continuous monitoring of AI decisions, but only 21 percent of enterprises have full visibility into their AI agent activities, according to Akto’s 2025 report. The remaining 79 percent are running models of unknown currency against an adversary landscape that evolves continuously.
The Policy Framework Fixing Both Problems
The governance answer emerging across serious enterprise deployments is not a binary choice between autonomous AI and human-reviewed everything. It is a tiered autonomy framework that assigns different levels of human oversight to different categories of action based on their risk profile.
Gartner’s four-mode SOC maturity model, presented by analyst Kevin Schmidt at the Gartner SRM Summit 2025, defines the progression:
Mode
Description
AI Role
Human Role
Mode 0
Manual operations
None
Everything
Mode 1
Semi-automated (SOAR, playbooks)
Predefined playbook execution
Approves and monitors
Mode 2
Augmented (AI copilot)
Recommends; enriches context
Approves all actions
Mode 3
Autonomous agents
Handles triage, hunting, some remediation
Oversees; handles novel/high-stakes cases
At Gartner’s Security Summit in June 2026, Gartner confirmed Mode 3 as the industry destination while explicitly warning about AI washing in vendor claims. Most enterprises currently operating on Mode 1 or early Mode 2 are being sold Mode 3 outcomes. The gap between those two things is exactly where the 2 percent problem lives.
The operational architecture that tiered autonomy translates to in practice looks like this. Triage and enrichment run fully autonomous: the volume is high, the risk of an individual wrong decision is relatively low, and this is where the efficiency gains live. Containment actions require human approval: isolating an endpoint, blocking a network segment, or disabling a user account has real operational consequences if wrong. Remediation is human-executed: the blast radius of a wrong remediation action is too high to automate.
Every AI action at every tier must be logged with an auditable reasoning chain. ISO/IEC 42001 compliance, NIS2 in Europe, and DORA for financial services are making this a regulatory requirement in addition to a governance best practice. CISOs in regulated industries who do not have AI governance documentation in place now are building compliance debt that will become costly to resolve under active regulatory scrutiny.
Pete Shoard, VP Analyst at Gartner and the credentialed industry voice on this topic, has been consistent on where the line is:
“If you think you can sack your SOC staff just because you’ve suddenly bought an AI function, I think you’re going to be soundly disappointed. AI won’t replace your security staff, so use it to enhance them and make them better in their jobs.”
Pete Shoard, VP Analyst, Gartner — Cybersecurity Dive, Gartner SRM Summit, June 2025
Shoard’s December 2024 Gartner research, “There Will Never Be an Autonomous SOC,” includes a warning that gets too little attention in vendor-led conversations: by 2030, 75 percent of SOC teams will experience erosion of foundational analysis skills due to AI over-dependence. The L1 analyst role, which is the training ground for senior investigators, disappears when AI handles Tier 1 and Tier 2 autonomously. A decade from now, when a truly novel threat requires human expert judgment, the pipeline of experienced analysts who would catch it may not exist.
The TIAA CISO, Upendra Mardikar, distilled the enterprise buyer position at the same Gartner conference:
“We don’t want complete autonomy. We have to have a human in the loop.”
Upendra Mardikar, CISO, TIAA — Cybersecurity Dive, Gartner SRM Summit, June 2025
Five Things CISOs Must Do Before Expanding AI Autonomy
The Intezer and AACT data, combined with the Arctiq case study and Gartner’s maturity framework, point to five concrete operational changes that should precede any expansion of AI autonomy in a SOC environment.
1. Stop Treating EDR “Mitigated” as a Closure Signal
The finding that 51 percent of confirmed compromised endpoints were already marked “mitigated” by EDR is operationally decisive. Security teams must add a forensic verification layer for cases where AI systems are considering closure. The EDR verdict is one data point. It is not ground truth. Any AI triage architecture that treats EDR “mitigated” as a final state is inheriting the EDR’s error rate on top of its own.
2. Define Bounded Autonomy Policies Before Deployment
The “automation gone wrong” case, where an AI-triggered response created a self-inflicted denial-of-service attack, happened because containment policies were not defined before the system went live. The question of which actions AI can execute without approval, which require human sign-off, and which are never automated must be answered in writing, reviewed by legal and compliance, and tested against tabletop scenarios before any autonomous capability is activated in production.
3. Track Mean Time to Conclusion for All Alerts, Not Just Escalated Ones
If your AI resolves 98 percent of alerts and your MTTD and MTTR look excellent, but the 2 percent error includes real threats hiding in low-severity backlogs, your dashboard is measuring speed rather than coverage. Mean Time to Conclusion must be tracked across the entire alert population, including the cases the AI autonomously closed. Auditing a statistically significant sample of AI-closed alerts monthly is the minimum viable oversight practice.
4. Build Model Drift Detection Into Your SOC AI Governance
Stale training data degrades AI SOC accuracy on a timeline that no vendor will proactively disclose to you. Define a retraining cadence based on your threat landscape velocity. Instrument the system to alert when false positive or false negative rates shift outside defined thresholds. ISO/IEC 42001 requires continuous monitoring of AI decisions. Build that monitoring before you need it, not after a breach investigation reveals the drift window.
5. Preserve the L1 Analyst Pipeline Deliberately
If AI handles all Tier 1 triage, the entry-level analyst role that trains the next generation of senior investigators disappears. Organizations running Mode 2 or Mode 3 autonomy need a deliberate career development path that keeps analysts engaged with real investigation work, not just AI oversight. The Gartner prediction that 75 percent of SOC teams will erode foundational analysis skills by 2030 is not a passive forecast. It is a consequence of a specific architectural decision that can be reversed with equally specific policy.
The Strongest Arguments Against the AI SOC Narrative
This article would not meet its own standard if it did not engage seriously with the case against the mainstream AI SOC story. Here are the strongest objections, stated plainly.
98 percent accuracy at scale is still a lot of wrong answers. At 10,000 daily alerts, 98 percent accuracy means 200 wrong triage decisions per day. The industry presents this as a success story. The correct question is: what is the false negative rate specifically, not the blended accuracy, and what types of threats are in that 2 percent? Advanced persistent threats and novel zero-day attacks are disproportionately likely to be in the error tail, because AI is trained on historical patterns and these threats are, by definition, outside historical patterns.
Vendor accuracy claims have self-serving methodologies. CrowdStrike’s 98 percent accuracy is measured against Falcon Complete expert decisions, meaning it is measured against itself. Intezer’s 98 percent is self-reported from its own customer telemetry. Neither has been validated by an independent third party against ground truth attack data. The only truly independent figure in available primary data is the AACT academic paper, which found a 1.36 percent false negative rate over 3.1 million alerts in a single managed SOC environment with characteristics that may not generalize to every deployment.
The AI creates a new, harder-to-find blind spot. A system tuned to eliminate false positives compensates by raising its detection threshold, which means it also starts suppressing low-signal real threats. Attackers learn to mimic the patterns the AI has been trained to ignore. This is not a theoretical concern. The SANS 2025 data confirms it is already happening. Stale model data is the leading driver of false positive spikes, which means organizations respond by raising the threshold further, which makes the blind spot larger.
Our read: the enterprise case for AI SOC automation is sound. The efficiency gains are real, the cost data is credible, and the alternative (a human-only model drowning in 10,000 daily alerts) is not viable. But the governance case has to be built with the same rigor as the technical case, and right now the governance conversation is at least two years behind the deployment conversation.
Frequently Asked Questions: AI SOC Automation
What percentage of SOC alerts can AI automatically resolve?
Real-world AI SOC platforms report autonomous resolution rates ranging from 61 percent (the peer-reviewed AACT system, 3.1 million alerts) to over 98 percent (Intezer, 25 million alerts). The range reflects differences in environment, alert type, and how “resolved” is defined. Enterprise deployments commonly target 40 to 60 percent automation as a conservative, auditable starting point before expanding autonomy.
What happens when AI gets a SOC alert wrong?
AI triage errors fall into two categories. False positives, meaning benign alerts incorrectly flagged, waste analyst time. False negatives, meaning real threats incorrectly closed, are the more dangerous failure. Intezer’s 2026 forensic analysis found that 1.6 percent of endpoints the AI cleared still had active Cobalt Strike or Mimikatz infections in memory. The correct policy response is tiered autonomy: AI handles routine closures independently, but containment actions require human approval.
Will AI replace SOC analysts?
No. Gartner’s December 2024 research explicitly titled “There Will Never Be an Autonomous SOC” states this is not a realistic outcome. AI automates Tier 1 and Tier 2 triage, eliminating repetitive alert-sorting work. Analysts shift to case validation, threat hunting, and AI oversight. The risk Gartner warns about is the opposite: by 2030, 75 percent of SOC teams may lose foundational analysis skills from over-reliance on automation.
What is “bounded autonomy” in AI cybersecurity?
Bounded autonomy means AI operates within customer-defined guardrails. Organizations control which triage actions the AI executes independently and which require human approval. CrowdStrike CTO Elia Zaitsev coined the term for Charlotte AI, launched February 2025. It sits between full autonomy (AI acts without human approval) and copilot mode (AI recommends; human always decides), and it is now the industry consensus model for production SOC AI deployment.
How much money does AI save in security operations?
IBM’s 2025 Cost of a Data Breach Report found that organizations using AI and automation extensively saved an average of $1.9 million per breach compared to those with no AI ($3.62 million versus $5.52 million average breach cost). They also cut breach lifecycles by 80 days. Faster detection means shorter dwell time, which directly reduces the total cost of a breach.
What is the false negative rate of AI SOC systems?
The most rigorous published figure comes from the peer-reviewed AACT system deployed in a real managed SOC: 1.36 percent false negative rate over 3.1 million alerts. CrowdStrike claims greater than 98 percent accuracy, implying roughly 2 percent combined error. Intezer reports 98 percent verdict accuracy across 25 million alerts. No vendor has published a standalone false negative rate independently verified by a third party.
What is model drift in cybersecurity AI?
Model drift occurs when an AI SOC system’s accuracy degrades because the threat landscape has changed but the model has not been retrained. Stale training data is the leading cause of false positive spikes in AI SOC tools, according to SANS 2025. In one documented case, an AI trained to dismiss certain low-level anomalies later failed to detect new attack techniques that resembled previously-benign behavior, creating a breach that a retrained model would have caught.
What is tiered autonomy in a SOC?
Tiered autonomy is the governance framework defining which SOC actions AI performs independently versus which require human approval. The consensus model: triage and enrichment are fully automated (high volume, low risk if wrong); containment actions require human sign-off (medium risk); remediation is human-executed (highest impact). Every AI action must be logged with an auditable reasoning chain for compliance with ISO/IEC 42001, NIS2, and DORA.
What You Now Know That You Didn’t Before
The AI SOC automation story is not a story about replacing human judgment. It is a story about redirecting it. AI handles the volume that was drowning analysts in noise. Analysts handle the cases that require genuine expertise. The failure is not in the model. The failure is in the governance architecture that surrounds it.
The specific risk that the Intezer data exposes is not that AI makes mistakes. Every triage system makes mistakes. The risk is that AI mistakes are invisible by default. When a human analyst incorrectly closes an alert, there is a record of the reasoning. When an AI closes it, the reasoning is there too, but nobody is reviewing it. The 51 percent of confirmed compromised endpoints that were already marked “mitigated” by EDR represent exactly this failure: a machine trusted a machine, and Cobalt Strike sat in memory undisturbed.
In the next 6 to 18 months, watch three things. First, whether the Gartner prediction about 30 percent of SOC leaders failing to integrate GenAI into production (due to hallucinations and governance gaps) materializes at the organizations that deployed most aggressively in 2025 without building the policy layer. Second, whether ISO/IEC 42001 and DORA enforcement creates a meaningful accountability mechanism for AI triage errors in financial services. Third, whether any vendor publishes independently verified false negative rates broken out by threat category, which would finally let buyers compare AI SOC platforms on the metric that actually matters.
If you are a CISO making a SOC AI decision right now, the question is not whether to deploy. The question is whether you have defined, in writing, what your system is allowed to close on its own. If the answer is “we configured the vendor defaults and moved on,” you have inherited someone else’s risk tolerance on behalf of your organization.
That is the policy this article is about.
Get The Neural Loop Every Week
Enterprise AI analysis, primary data, and the stories that matter to security and technology leaders. No noise. No vendor content.
Subscribe Free at NeuralWired.com
AI Threat Detection Cuts Breach Costs by $1.9M. So Why Are 68% of Enterprise SOCs Still Flying Blind?AI Cybersecurity • Enterprise SOC
AI Threat Detection Cuts Breach Costs by $1.9M. So Why Are 68% of Enterprise SOCs Still Flying Blind?
By NeuralWired Editorial • June 22, 2026 • 14 min read
Here is the problem, stated as plainly as possible. The average enterprise cybercriminal gains initial network access and begins moving laterally in 29 minutes. The average SOC analyst, working a manual triage queue packed with over 10,000 daily alerts, takes significantly longer than that just to confirm an alert is real.
That is not a performance failure. That is a structural mismatch between the speed of modern intrusion and the design limits of human-pace security operations. And the data makes the gap measurable: AI-augmented SOC environments have demonstrated a 50% reduction in mean time to detect (MTTD) and a 60% drop in manual triage workload. Non-autonomous AI agents in documented deployments reduced investigation times from 30-plus minutes to under two minutes per incident.
So the question this article sets out to answer is not whether AI threat detection works. The data on that is clear. The question is why approximately 68% of enterprise security operations centers are still not using it at scale.
Key Data Point
IBM’s 2025 Cost of a Data Breach Report found organizations using AI and automation extensively pay $3.62 million per breach on average. Those without pay $5.52 million. That $1.9 million gap is the largest single-technology cost difference IBM has ever recorded in this study’s history.
The Detection Gap Nobody Wants to Admit
Traditional SOC architecture was designed for a threat landscape that no longer exists. In the model that most enterprises still run, Tier 1 analysts review alerts manually, escalate to Tier 2 for investigation, and escalate further to Tier 3 for complex incidents. This model worked when attacks unfolded over hours or days. It doesn’t work when the initial-access-to-lateral-movement window is measured in minutes.
The alert volume problem compounds this. Modern enterprise SOCs process an average of 10,000 or more alerts per day, with false positive rates hovering around 45%. The SANS Institute’s 2025 survey found 73% of security teams cite false positives as their primary detection challenge, not insufficient tooling, not budget. False positives. The noise is so overwhelming that up to 40% of alerts go uninvestigated entirely.
Analyst burnout cycles average 18 months before turnover. That number tells you everything about what it means to be a Tier 1 SOC analyst in 2026: you are drowning in 100,000-plus daily alerts where between 1% and 5% are real threats, you cannot distinguish signal from noise fast enough to matter, and the job grinds people down until they leave.
10,000+Average daily alerts per enterprise SOC, with a 45% false positive rate
40%Share of security alerts that go completely uninvestigated
18 mo.Average analyst burnout cycle before SOC Tier 1 turnover
50%MTTD reduction demonstrated by AI-augmented SOC operations
This is the structural problem that AI threat detection is designed to solve. Not by replacing analysts. By absorbing the volume of mechanical triage work that is consuming their capacity and preventing them from doing the judgment-based work only they can do.
When the Attacker Moves in 29 Minutes
The CrowdStrike 2026 Global Threat Report, published February 24, 2026, documents something that should recalibrate how every CISO thinks about incident response timelines.
The average eCrime breakout time in 2025, defined as the elapsed time from initial access to lateral movement, dropped to 29 minutes. That represents a 65% increase in attacker speed from 2024. The fastest observed intrusion moved from access to lateral movement in 27 seconds. In one documented case, data exfiltration began within four minutes of initial compromise.
“This is an AI arms race. Breakout time is the clearest signal of how intrusion has changed. Adversaries are moving from initial access to lateral movement in minutes. AI is compressing the time between intent and execution while turning enterprise AI systems into targets. Security teams must operate faster than the adversary to win.”
Adam Meyers, Head of Counter Adversary Operations, CrowdStrike
The 29-minute average is an organizational benchmark, not a theoretical worst-case. If your incident response workflow takes longer than 29 minutes from detection to analyst action, you have already ceded the lateral movement window to the attacker. In a significant share of intrusions, the attacker has established persistence and begun moving toward their objective before the alert even surfaces in the SOC queue.
The attacker speed story gets worse when you consider what those attackers are now equipped with. AI-enabled adversary operations increased by